Risk and Governance squad

AI DevSecOps engineer with change evidence built in

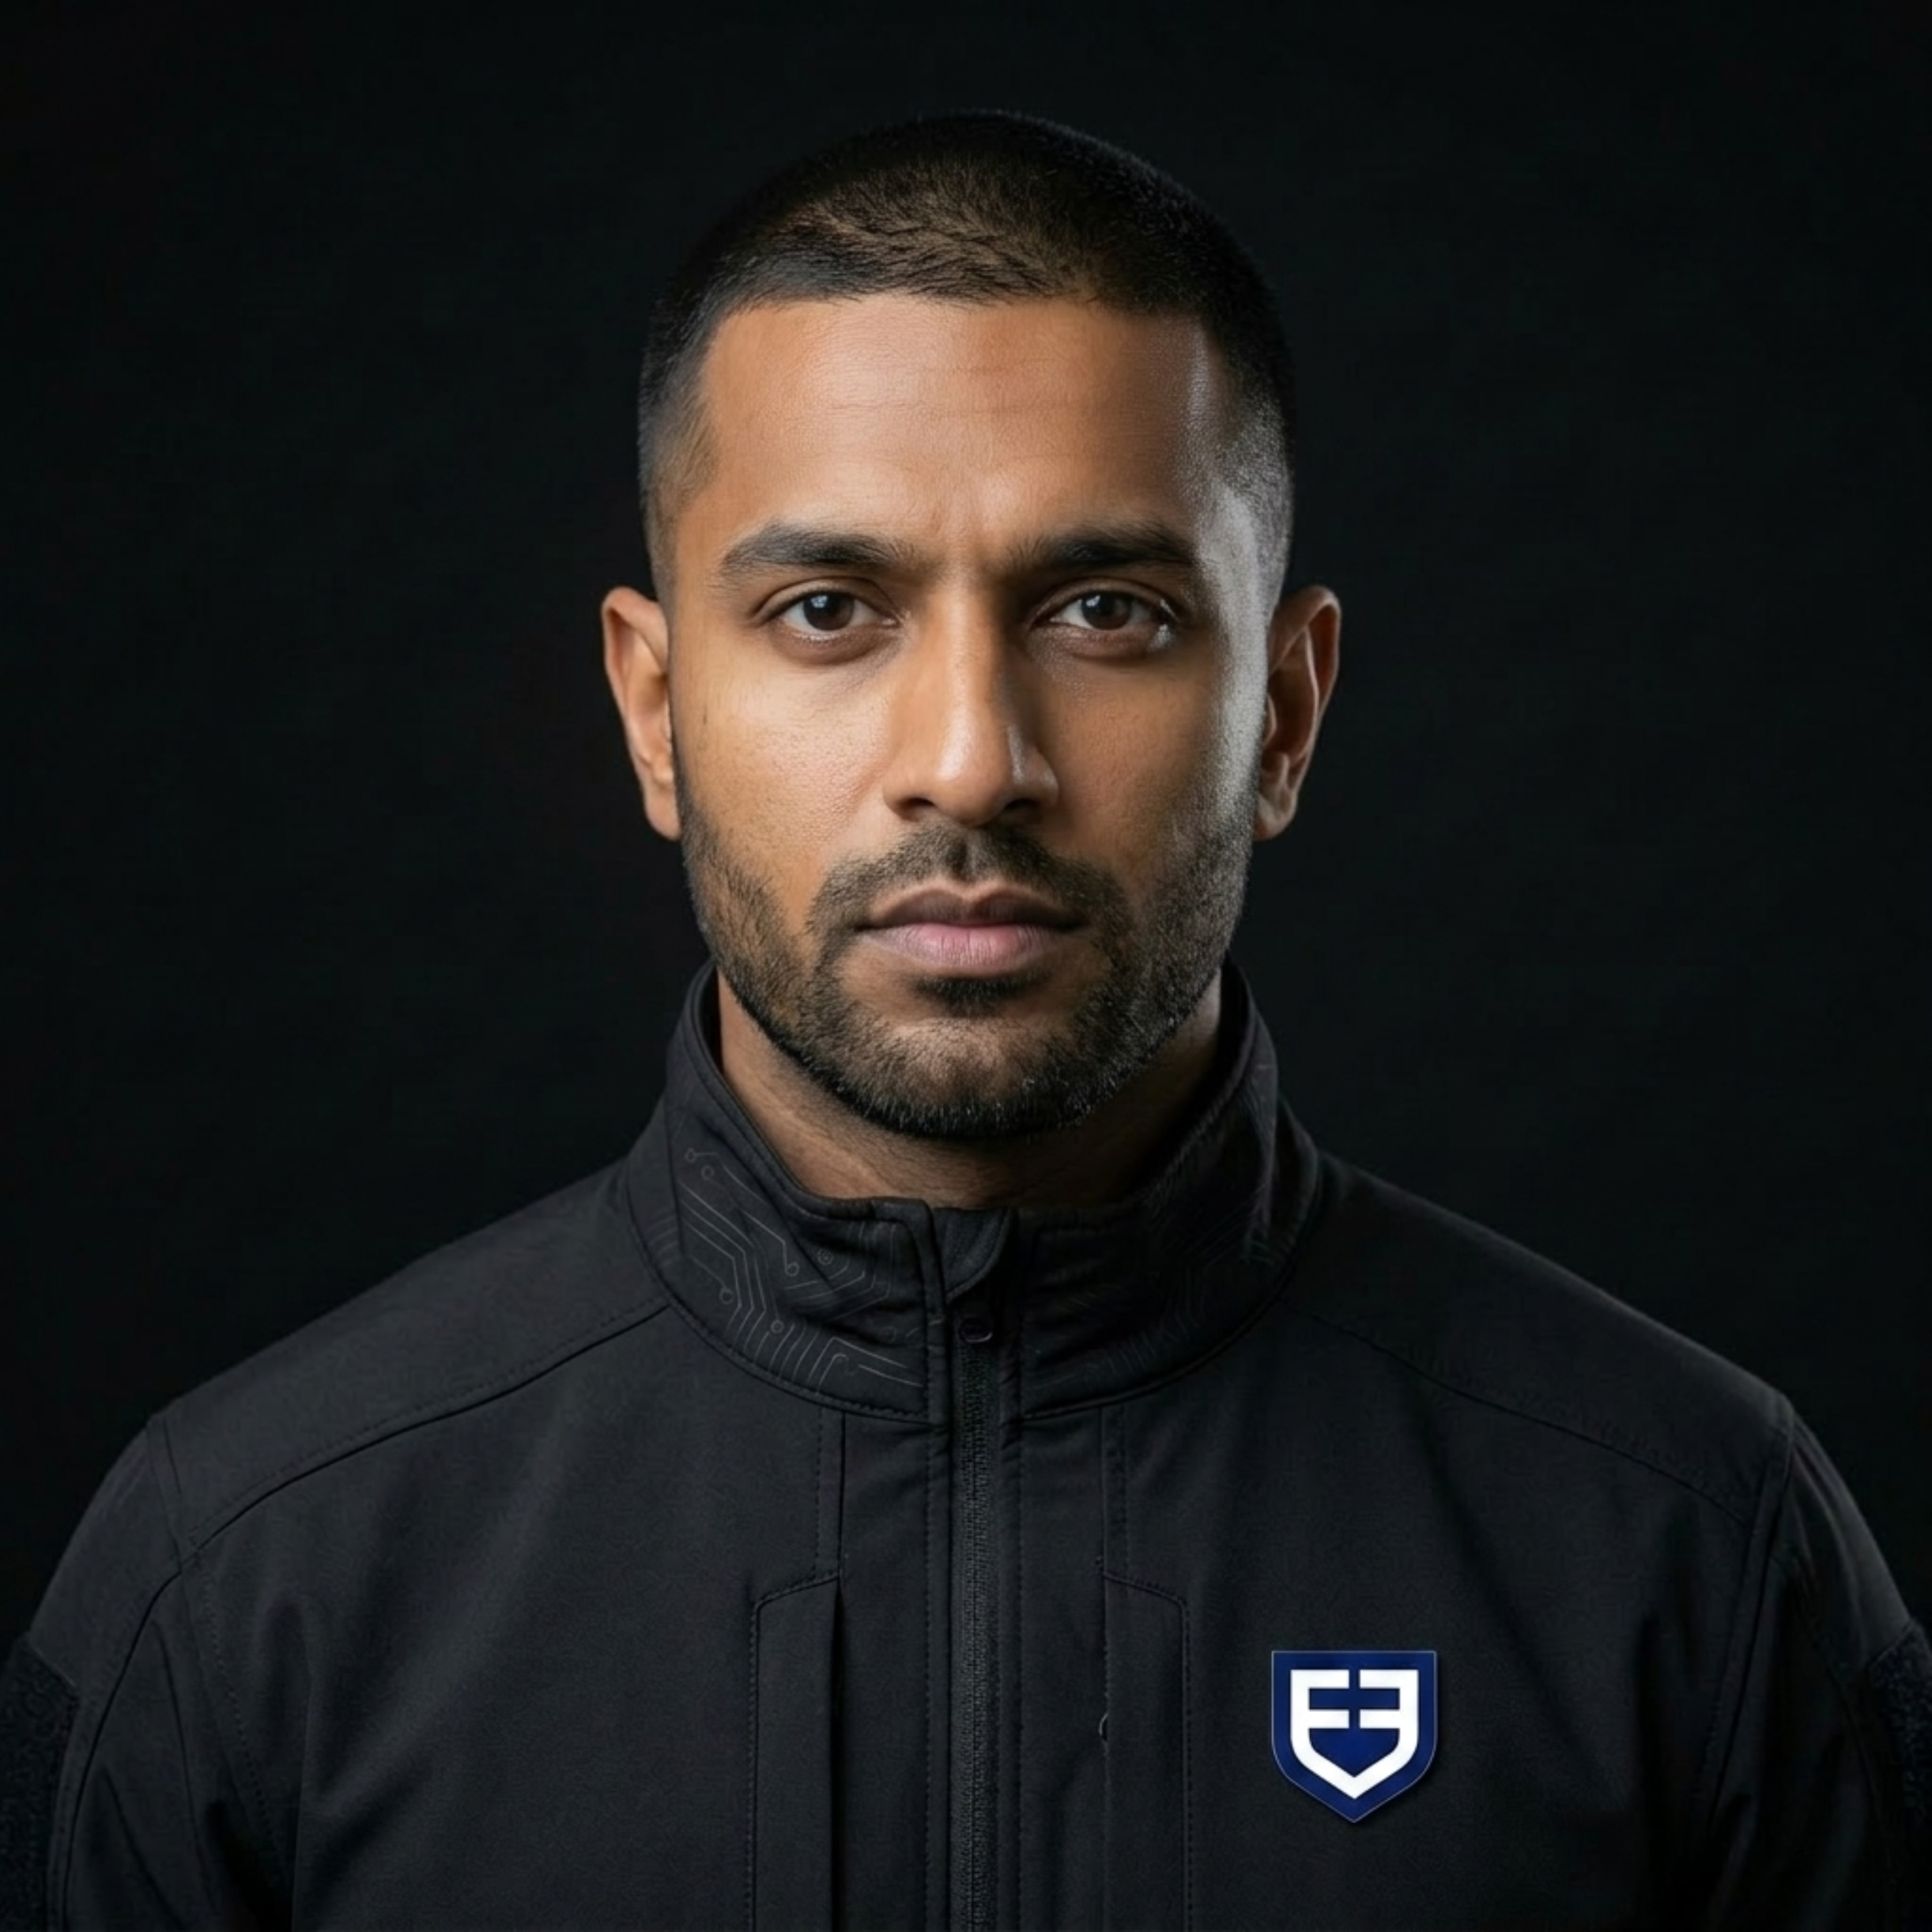
Devon Pulse, Lead AI DevSecOps Pipeline Architect, an AI agent by FluxForceDevon Pulse — Lead AI DevSecOps Pipeline Architect

Devon Pulse is an AI agent that scans code, dependencies and release pipelines for vulnerabilities and exposed secrets before anything ships. He focuses on the systems your compliance team relies on, such as monitoring, screening and case management. Findings go to your engineers, and every release leaves a change record an examiner can follow.

Devon Pulse
Devon Pulse, Lead AI DevSecOps Pipeline Architect, an AI agent by FluxForce
Release 7.3 scanned
IllustrativeFlagged for review
Finding severity · high
Flag explained
“API key in a config file; dependency with a known vulnerability.”
DORAPCI DSS v4.0.1
REPORTS TO
Your Head of Engineering, with the CISO informed
Shadow mode first
How Devon works with your team
Shadow mode
first: nothing acts until you say so
3 bands
of autonomy you configure
Every decision
has a replayable record
1 per agent
kill switch
SaaS · on-prem · hybrid
deployment
Product controls, not performance claims. Performance is measured on your data, in shadow mode.
The problem

Fast releases, thin evidence for the systems compliance runs on

Your teams ship changes to screening rules, monitoring scenarios and case tools every week. Each release can carry a vulnerable library or a leaked key. When an examiner asks how a change was tested and approved, the answer is spread across tickets, chat threads and pipeline logs.

RELEASE QUEUE
Weekly

changes to compliance systems

Each one needs a record.

Secrets risk

Keys end up in the wrong place

Credentials for screening APIs, data stores and payment gateways get pasted into config files and scripts. One leaked key can expose customer and case data.


Dependency risk

Libraries you didn't write

Most code in a modern release comes from open-source packages. A known vulnerability in one of them is your vulnerability once it ships.

Evidence gap

Change control nobody can replay

Examiners ask who approved a change to a monitoring scenario, what was tested and what was found. Rebuilding that from pipeline logs takes days.

Job description

What Devon Pulse does Job description

Devon Pulse is a Lead AI DevSecOps Pipeline Architect. He sits in your release pipeline, scans what's about to ship and records what was found and who signed off.

AI AGENT · RISK AND GOVERNANCE SQUAD
Devon Pulse, Lead AI DevSecOps Pipeline Architect, an AI agent by FluxForce
DEVON PULSE
Lead AI DevSecOps Pipeline Architect
REPORTS TO
Your Head of Engineering, with the CISO informed
WORKS WITH
Your source code repositories, CI/CD pipelines, package registries and ticketing system
DEPLOYED
Shadow mode first, then the autonomy you set
KEY RESPONSIBILITIES
01Scan code and configuration for exposed secrets, insecure patterns and risky changes before release
02Check dependencies against known vulnerability data and flag the ones that matter for your systems
03Send findings to the engineer who made the change, with the file, the risk and a suggested fix
04Hold a release for review if you set it to, when a high-severity finding is open
05Keep a change record for each release: what changed, what was scanned, what was found and who approved it
AUTONOMY MODEL
Low risk
Can log and close low-severity findings, if you allow it
LOW
Medium risk
Goes to the engineering lead by default
MEDIUM
High risk
Always goes to the engineering lead and CISO
HIGH
You set the threshold per rule.
Kill switch: Turn Devon off at any time
Shadow mode

What to measure in shadow mode on your own pipelines

We don't publish detection rates from our own tests. Measure what Devon Pulse finds in your repositories and pipelines, next to your current scanners and reviews.

01
Findings confirmed
Share of Devon's findings your engineers agree are real.
02
Secrets caught before release
Exposed credentials Devon found before they shipped.
03
Missed-finding review
Any issue found later, in production or by a pen test, that Devon didn't flag. Read this first.
04
Time to fix
Hours from a finding to a merged fix, by severity.
05
Noise level
Findings engineers close as not relevant, by check type.
06
Releases with a full record
Share of releases with scans, findings and approvals on record.
07
Compliance system coverage
Share of monitoring, screening and case code under scan.
08
Decisions with evidence
Share of release approvals with a replayable record. The target is all of them.
Shadow mode results belong to you. We agree the repositories, the time window and who reviews the findings before the trial starts.
How it works

How AI DevSecOps works with Devon Pulse

Devon Pulse connects to your repositories and pipelines through their APIs. Your release process stays your own.

01

Ingest

Commits, pull requests, build manifests, dependency lists and pipeline events arrive from your source control and CI/CD tools.

02

Scan

Devon runs deterministic checks for secrets and known vulnerabilities, and reviews changes for insecure patterns. Code paths in monitoring, screening and case systems get extra attention.

03

Route

Your autonomy settings decide what happens next. Low-severity findings can close with a reason if you allow it. Medium findings go to the engineering lead by default. High-severity findings always go to the engineering lead and CISO, and can hold the release for review if you set it to.

04

Record

Every release gets a change record: the diff, the scans, the findings, the fixes and the named approver. It goes into tamper-evident evidence storage, ready for an examiner.

Want to see this on your data?

Run Devon Pulse in shadow mode on your pipelines. He scans and records, and no release is held. Compare his findings with your current tools before you switch anything on.

Request a shadow mode trial
Compliance and regulatory mapping

Regulatory frameworks Devon Pulse supports

Devon doesn't make you compliant. He produces the change and security evidence these frameworks expect you to keep.

DORA
EU financial entities manage ICT risk, including change. Devon's release records show what changed and how it was checked.
NYDFS Part 500
New York's cybersecurity regulation covers application security. Devon's scans and records support that programme.
PCI DSS v4.0.1
Secure software development for systems that touch card data. Devon's records support your assessment.
OWASP API Security Top 10 (2023)
Common API weaknesses. Devon checks for them in the services your compliance systems expose.
OWASP Top 10 for LLM Applications
Risks specific to AI features. Devon checks prompts, model calls and output handling in your code.
ISO/IEC 27001
A standard many banks align to. Devon's evidence maps to secure development and change management controls.
Analyst view

What your engineering and audit teams see

Security findings before release, and a change record after.

BEFORE DEVON PULSE
Secrets found after they've shipped
Dependency alerts nobody triages
Scanner output separate from compliance context
Change approvals spread across tools
Evidence rebuilt by hand for each exam
AFTER DEVON PULSE
Secrets flagged before release
Dependency findings ranked for your systems
Extra checks on monitoring, screening and case code
One change record per release with a named approver
Every release replayable for an examiner
Options

How the options compare

CRITERIA Manual code reviewStandalone code scanner Devon Pulse, Lead AI DevSecOps Pipeline Architect, an AI agent by FluxForceDevon Pulse
When issues are found When a reviewer spots themOn each scan On each change, before release
Who decides ReviewerScanner rules, then engineer Engineering lead and CISO, inside bands you set
Knows which systems compliance relies on If the reviewer doesNo Yes, those code paths get extra checks
Change record for examiners Review commentsScan reports One record per release: diff, scans, findings, approver
Cover across all repositories Limited by reviewer timeYes Yes
Where it's weaker Slow and depends on who reviewsNoisy, with no compliance context Needs tuning to your codebase, and won't replace design reviews or penetration tests
Trust Builders

Built for Regulated Financial Institutions

01

Configurable autonomy

Low risk can run on its own if you allow it. Medium risk goes to a person by default. High risk always goes to a person. You set the bands per rule, channel and transaction type.

02

Kill switch

Turn Devon off without touching the other agents or your core systems. The switch, and who used it, is stamped on the record.

03

Shadow mode

Run Devon on live data with nothing blocked or closed. Compare the calls with your team's before anything changes.

04

Explainability

Every decision answers why, in plain English, with the signals and the rule or policy behind it.

05

Audit trail

Each decision is stored with its inputs, its reasoning and the person who approved it, in tamper-evident evidence storage.

06

No migration

Agents connect beside your systems through APIs. Your core banking, screening and case tools stay where they are.

Questions? We Have Answers

Frequently Asked Questions

FluxForce

Still have questions?

Talk to the people who build the agents. We'll answer per capability, yes or no.

Devon Pulse scans code, dependencies and pipelines for vulnerabilities and exposed secrets before release. He gives extra attention to the systems your compliance team relies on and keeps a change record for every release that an examiner can follow.

He can hold a release for review if you set it to, when a high-severity finding is open. A named person decides whether it ships. Low-severity findings can close with a reason only where you allow it. A kill switch turns Devon off without touching your pipelines.

No. Devon can read results from scanners you already run and adds compliance context, ranking and a change record on top.

Devon scans your repositories and pipelines and records what he finds, but no release is held. Your engineers compare his findings with their current tools before you turn on any autonomy.

Read access to your source repositories, CI/CD pipeline events, dependency manifests and ticketing system. He doesn't need production data.

Examiners often ask how a change to a monitoring scenario or screening rule was tested and approved. Devon's change record shows the diff, the scans, the findings and the named approver in one place.

FluxForce runs as SaaS, on-premise or hybrid, built on Microsoft Azure. We agree data residency and which components run inside your environment during deployment design, before any data moves.

Shadow mode trial

See Devon on your data before anything changes

Run Devon Pulse beside your current process. He works on your live data and records every call, and nothing is blocked, closed or sent until you decide.

  • Runs in shadow mode on your own data, next to your team
  • You agree the metrics, the time window and who reviews the results
  • Kill switch and a replayable record of every decision from day one
  • SaaS, on-premise or hybrid, with data residency agreed up front

Shadow mode results belong to you.

Take the first step

AI agents that prepare the case. Your team makes the call.

Start with one workflow in shadow mode, then decide how much each agent does on its own.

How we start
Discovery and scoping
Integration beside your systems
Shadow mode
Controlled autonomy
Govern and improve