
Match noise
One name, a dozen spellings
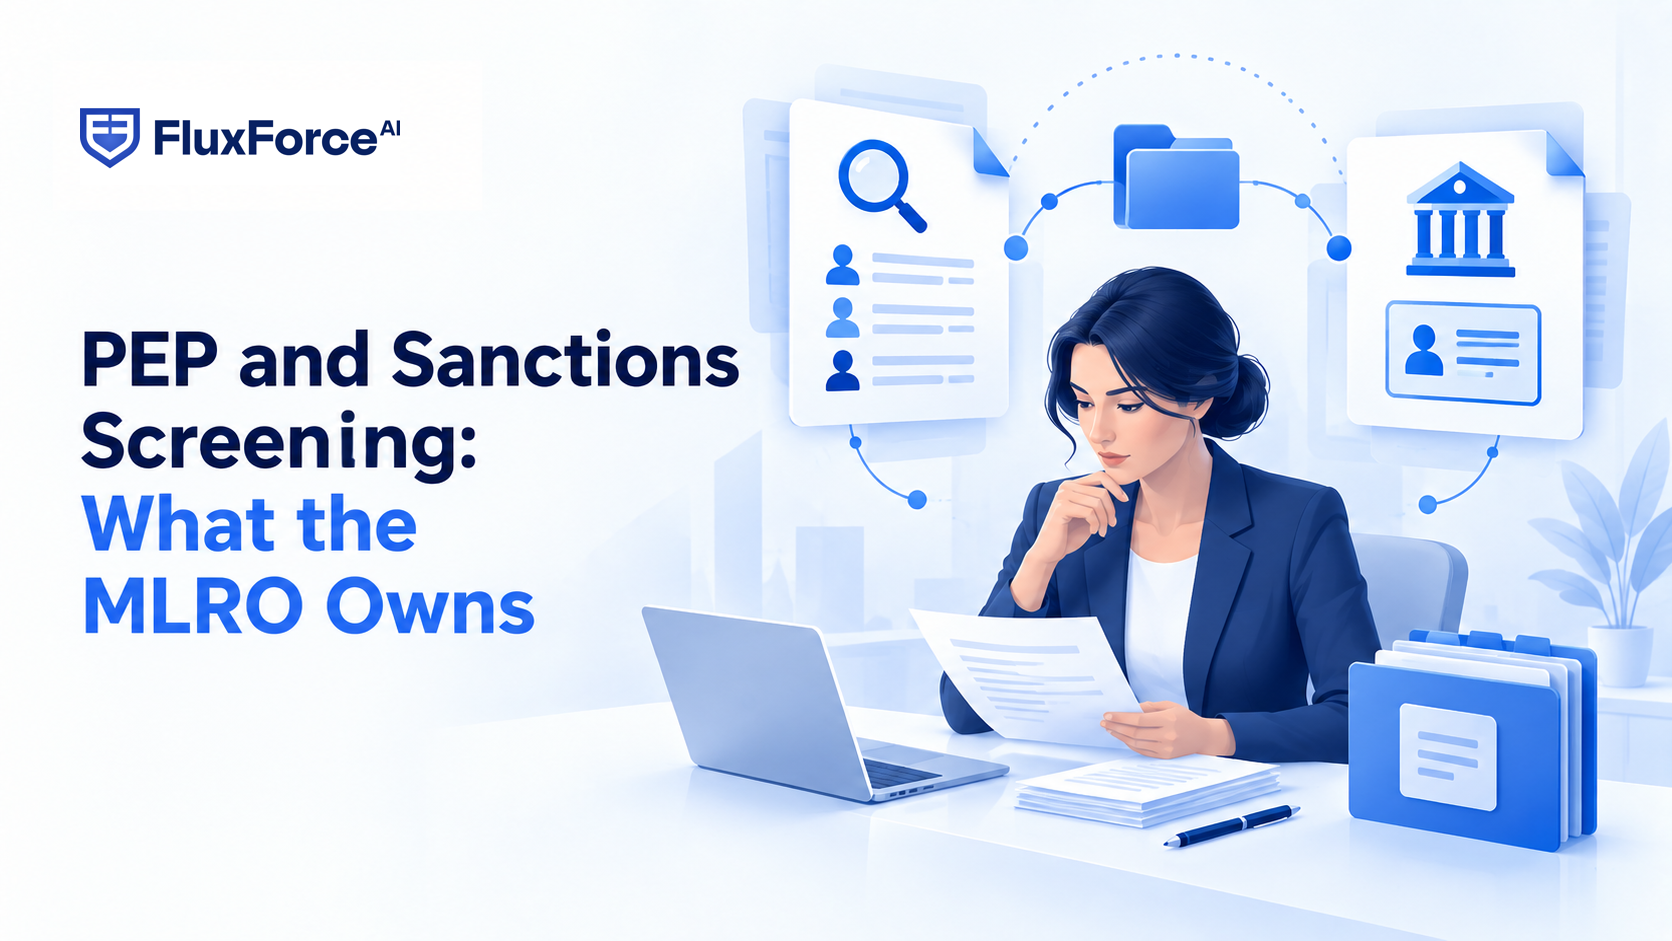
Arabic, Cyrillic and Devanagari names transliterate several ways. Fuzzy matching catches them all, and an analyst has to check date of birth, nationality and address for each one by hand.



 28 specialized agentsAll systems operational
Ready to transform your security infrastructure?
Explore our complete agent library and request a custom demoView All SolutionsAiden FluxSenior AI Fraud Risk AnalystRhea LedgerSenior AI KYC/AML Compliance DirectorNova SentinelLead AI Zero Trust Security ArchitectIris VermaAI Verification Specialist
 Oscar GraySenior AI OSINT Intelligence Director
 Bella NovaAI BNPL Risk Analyst28 specialized agentsAll systems operational
Ready to transform your security infrastructure?
Explore our complete agent library and request a custom demoView All Solutions28 specialized agentsAll systems operational
Ready to transform your security infrastructure?
Explore our complete agent library and request a custom demoView All SolutionsRhea Ledger — Senior AI KYC/AML Compliance Director
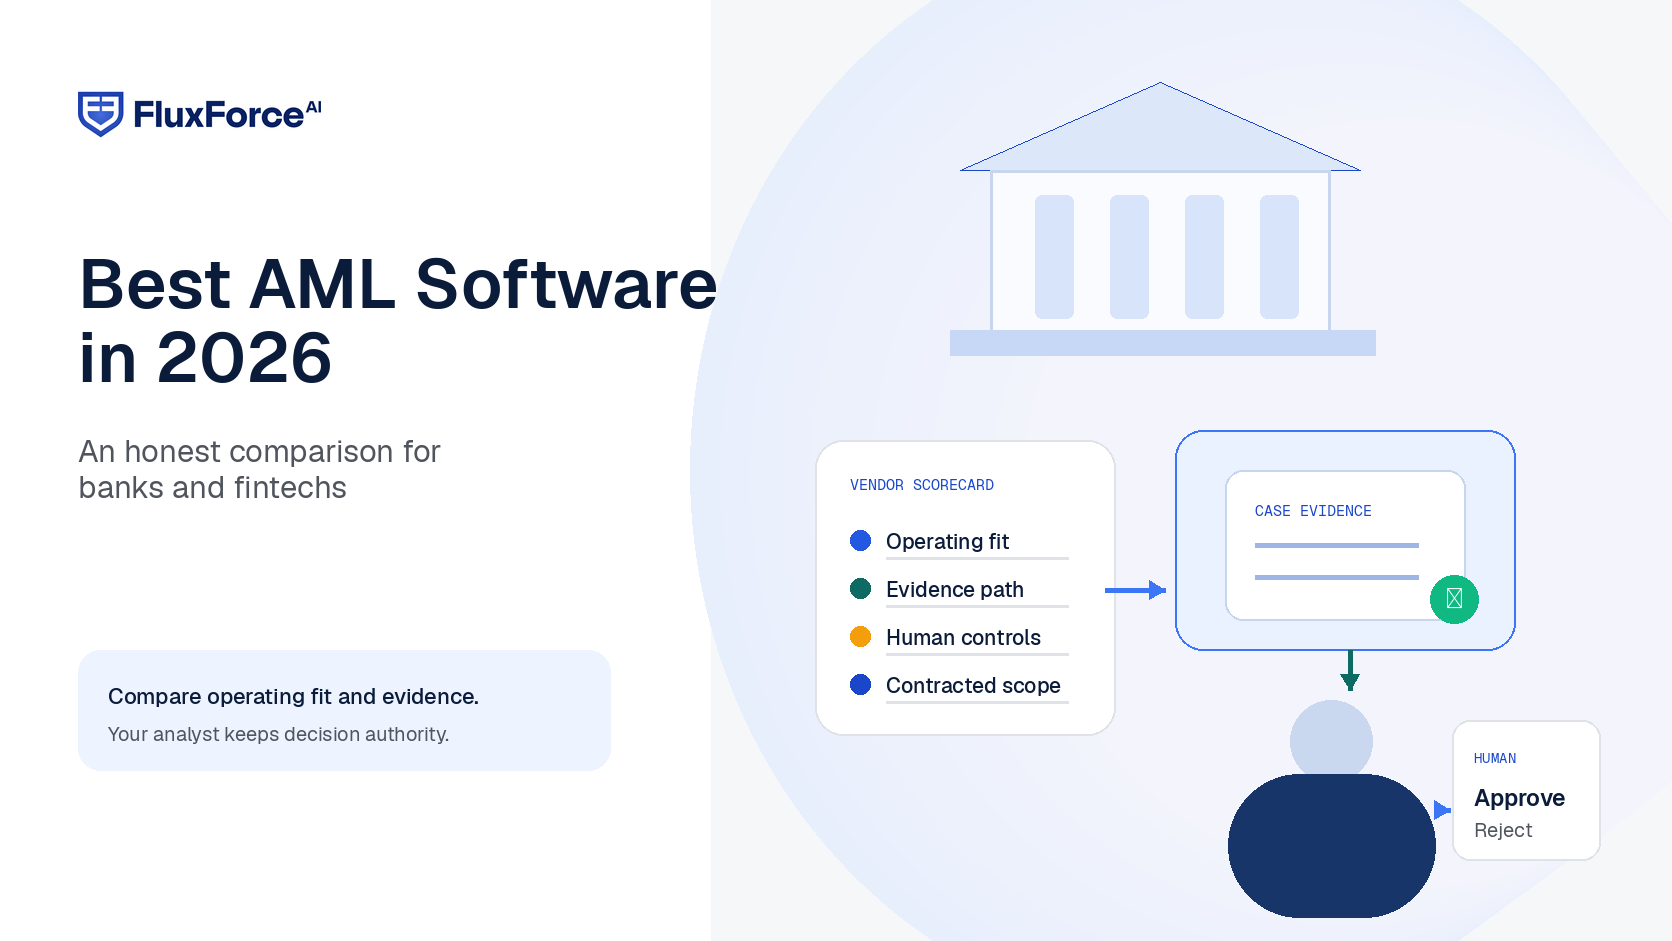
Rhea Ledger is an AI agent that screens customers against sanctions and PEP lists, resolves look-alike names across scripts, refreshes KYC when something actually changes and rates customer risk on your own factors. She drafts STR, SAR and CTR content for your MLRO to review. Your team signs off.
Rhea Ledger is a Senior AI KYC/AML Compliance Director. She sits beside your screening, onboarding and case management systems, works the match queue and prepares what your MLRO needs to sign off.
| CRITERIA | Manual match review | Screening tool only | Rhea Ledger |
|---|---|---|---|
| Time to first results | A hiring and training cycle | List setup and threshold tuning | Shadow mode on your live data |
| Who decides | Analyst | Match threshold, then analyst | Analyst, inside autonomy bands you set |
| Why a match was closed | Analyst notes, varies by person | Match score only | Plain-English reason with the fields compared |
| KYC refresh trigger | Calendar and ad hoc requests | Calendar | Events in the customer's data, plus your calendar |
| Report drafting | Written by hand | Not covered | Drafted for MLRO review and approval |
| Where it's weaker | Cost grows with match volume | High match noise across scripts | Only as good as your customer data and lists, and needs past dispositions before you trust the bands |
Rhea's files get more complete when other agents add what she can't see on her own.
Brings transaction behaviour and fraud scores into the customer risk picture.
Meet AidenAdds adverse media with a confidence level, with namesakes already filtered.
Meet OscarConfirms the person behind the record is real before screening starts.
Meet IrisWhat we're learning about AML, fraud and the evidence examiners ask for.

Talk to the people who build the agents. We'll answer per capability, yes or no.
It works the screening and due diligence queue that analysts handle today. Rhea Ledger resolves sanctions and PEP matches, triggers KYC reviews when customer facts change, rates customer risk on your factors and drafts suspicious activity reports. Your analysts and MLRO review and approve the outcomes.
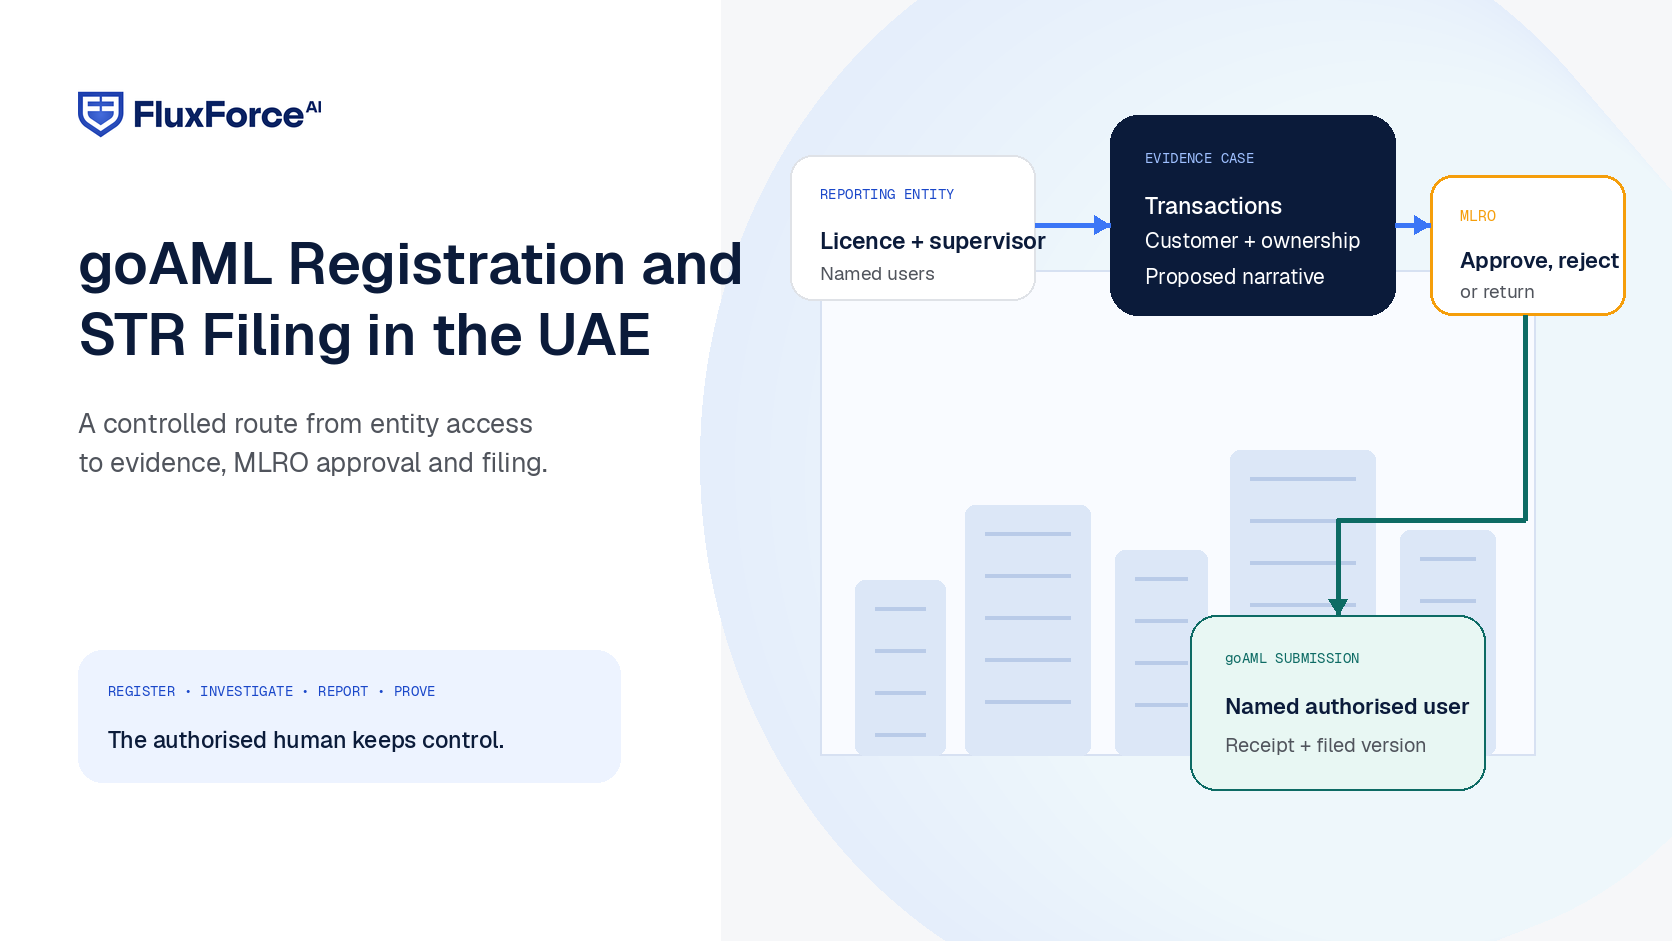
No. Rhea drafts the content with the supporting facts attached. Your MLRO or Principal Officer edits it, approves it and submits it through your usual channel, such as goAML, FINnet or FinCEN's system.
Only clear namesakes, only in the risk bands you allow, and each closure carries a recorded reason. Likely true sanctions matches always go to an analyst. A kill switch turns Rhea off without touching your other systems.
Rhea compares transliteration variants alongside date of birth, nationality, address and known associates. A name match on its own isn't enough to close or escalate. The reason she gives lists which fields agreed and which didn't.
No. She works with the lists and hits your current provider produces, and with your onboarding and core systems. You keep your lists and add Rhea's resolution and drafting on top.
Rhea works your live match queue and drafts reports, but nothing is closed or sent. Your analysts keep working as they do today, and you compare Rhea's calls with theirs. You decide whether, and where, to switch on any autonomy afterwards.
FluxForce runs as SaaS, on-premise or hybrid, built on Microsoft Azure. We agree data residency and which components run inside your environment during deployment design, before any data moves.