

Listen To Our Podcast🎧
What does AML/CFT compliance in Mauritius require?
A Mauritian bank, financial institution or other reporting person takes its core AML/CFT duties from the Financial Intelligence and Anti-Money Laundering Act 2002 (FIAMLA). The Act tells it to register with the Financial Intelligence Unit (FIU), assess and document its money laundering, terrorism financing and proliferation financing risks, set policies that senior management approves, apply customer due diligence (CDD) and identify beneficial owners, keep records for at least seven years and report suspicious transactions to the FIU within five working days of the suspicion arising. The Bank of Mauritius supervises banks and the other institutions it licenses. The Financial Services Commission (FSC) supervises the non-bank financial services sector and global business. Inside the institution, the Money Laundering Reporting Officer (MLRO) receives internal disclosures and decides what goes to the FIU.
This guide is for MLROs and compliance heads at Mauritian banks, FSC licensees, global business companies and the groups that own them. It works from FIAMLA as amended to 2026, the Bank of Mauritius AML/CFT guideline, FIU guidance, FSC guidance and the national AML/CFT strategy for 2026 to 2029, as they stood on October 14, 2026. It is a practical reading of those texts, not legal advice for a specific entity.
- Which body supervises which institution, and what the FIU receives.
- What the 2026 FIAMLA amendments changed for risk assessments, policies and beneficial owners.
- How the five-working-day STR route runs from internal disclosure to goAML.
- What the MLRO, Deputy MLRO and compliance officer each own.
- How to map CDD and evidence responsibility between a global business company and its management company.
Request a Mauritius AML/CFT program walkthrough
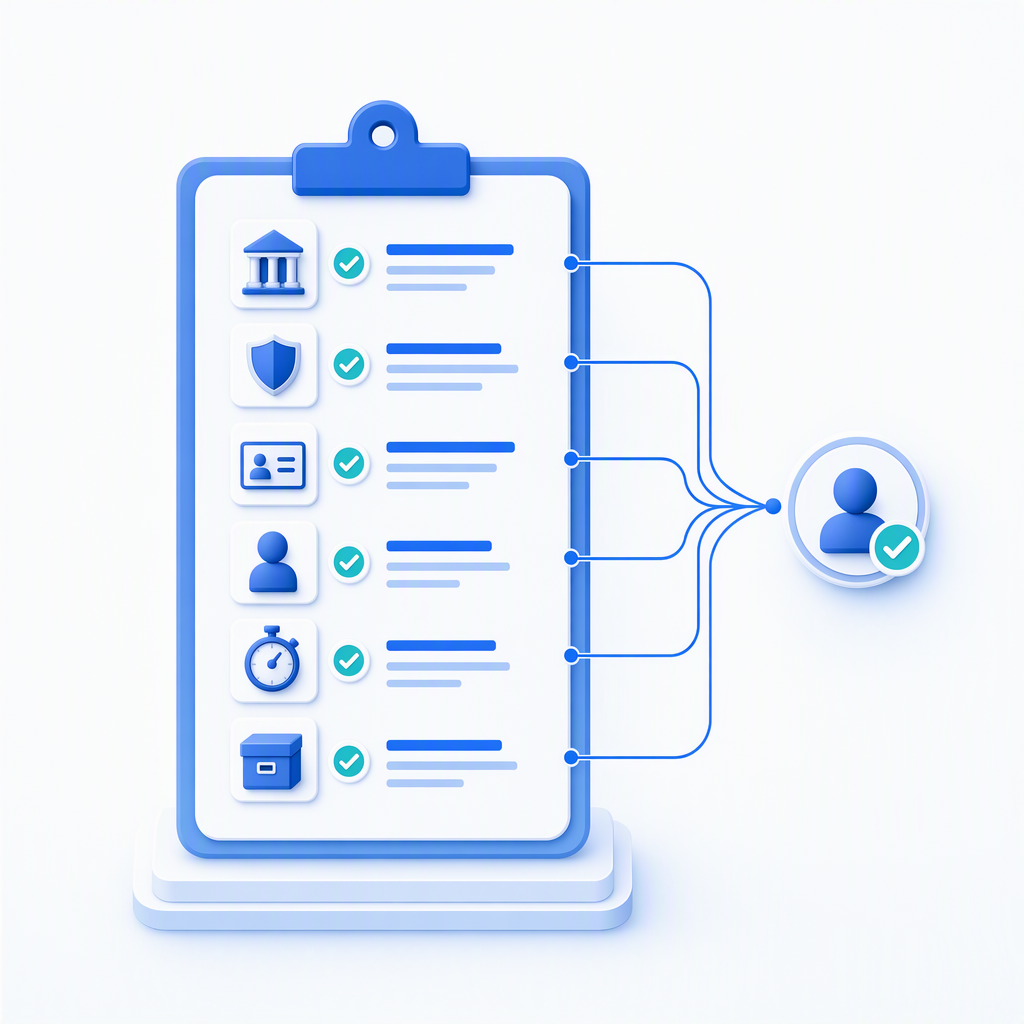
A Mauritian reporting person must register with the FIU, document its money laundering, terrorism financing and proliferation financing risks, apply CDD and identify beneficial owners, keep records for at least seven years and report suspicious transactions to the FIU within five working days. The Bank of Mauritius supervises banks and the FSC supervises non-bank financial services and global business, while the MLRO decides what is reported.
Who supervises AML/CFT compliance in Mauritius?
FIAMLA names the Bank of Mauritius and the Financial Services Commission as supervisory authorities, alongside the Registrar of Co-operative Societies. Professional bodies and the FIU itself act as regulatory bodies for the designated professions, such as accountants, law firms, notaries, real estate agents and dealers in precious metals.
- FIAMLA names the Bank of Mauritius and the Financial Services Commission as supervisory authorities, alongside the Registrar of Co-operative Societies. The Bank of Mauritius supervises banks, non-bank deposit-taking institutions, cash dealers, money lenders and payment system licensees. The FSC supervises non-bank financial services licensees and global business companies. Every reporting person registers with the FIU and files suspicious transaction reports with it through goAML. Under section 22 of FIAMLA, the FSC forwards information about a possible money laundering offence or suspicious transaction to the FIU. The UN Consolidated List is published on the FIU website and sent to reporting persons registered on goAML. Professional bodies and the FIU act as regulatory bodies for the designated professions, and FSC licensees screen clients at onboarding, at intervals, on trigger events and on every list update.
The Bank of Mauritius supervises banks, non-bank deposit-taking institutions, cash dealers, money lenders and payment system licensees. Its AML/CFT guideline describes the Bank as "the designated AML/CFT supervisory authority of financial institutions under its purview". The guideline covers banks, non-bank deposit-taking institutions, cash dealers and money lenders licensed under the Banking Act 2004, plus licensees under the National Payment Systems Act 2018.
The FSC supervises non-bank financial services licensees and global business companies. The FSC describes itself as the integrated regulator for the non-bank financial services sector and global business. When it supervises its licensees, the FSC looks at market conduct, AML/CFT requirements and corporate governance. It also has a memorandum of understanding with the FIU. Under section 22 of FIAMLA, the FSC forwards information about a possible money laundering offence or suspicious transaction to the FIU.
The FIU is the national body that receives suspicious transaction reports. Every reporting person registers with the FIU and files suspicious transaction reports with the FIU. The UN Consolidated List is published on the FIU website and sent to reporting persons registered on goAML. The FSC's targeted financial sanctions page says licensees should screen clients when a relationship starts, at regular intervals, on trigger events such as a change of directors or owners, and whenever the UN Consolidated List or the list of designated parties is updated.
What changed in 2026?
Act No. 3 of 2026 amended FIAMLA with effect from April 18, 2026. The changes that matter most for a compliance program are these:
- Section 17 now requires reporting persons to identify, assess and understand proliferation financing risk alongside money laundering and terrorism financing risk. A new subsection lets that proliferation financing work sit inside an existing targeted financial sanctions or compliance program.
- Section 17A was replaced. Policies, controls and procedures must now mitigate the risks found in the institution's own risk assessment or in the national risk assessment.
- Section 17E was replaced. The beneficial owner of a legal person is the natural person who ultimately owns or controls the customer, including anyone exercising ultimate effective control. If no such person can be identified, the reporting person identifies the senior managing official.
In February 2026 the Ministry of Financial Services and Economic Planning published the National Strategy for Combatting Money Laundering and Countering the Financing of Terrorism 2026-2029. It builds on the Second National Risk Assessment, published in May 2025, which kept the overall money laundering risk at Medium-High and moved terrorism financing risk from Medium to Medium-Low. Your own risk assessment has to take that national assessment into account, so read the sector findings that apply to you.
Is Mauritius on the FATF grey list?
No. The FSC reports that at its plenary on October 21, 2021, the FATF concluded Mauritius was no longer subject to increased monitoring. After five follow-up reports, Mauritius is Compliant on 26 of the 40 FATF Recommendations and Largely Compliant on the other 14. Its next mutual evaluation under the Eastern and Southern Africa Anti-Money Laundering Group (ESAAMLG) is scheduled for 2028. That evaluation will test effectiveness, so expect supervisors to ask for evidence that controls actually work.
What must every reporting person do under FIAMLA?
The duties in Part IV of FIAMLA form one chain. The risk assessment drives the policies, controls and procedures. The policies set the depth of customer due diligence for each customer. Customer due diligence feeds ongoing monitoring of the relationship. Every CDD result goes into records kept for at least seven years. If one link is missing, an examiner can't follow the institution's reasoning from risk to decision.
- Your risk assessment covers money laundering, terrorism financing and proliferation financing and must take the national risk assessment into account. Before launching a new product, business practice or new or developing technology, including AI tooling, you must assess the risks it may bring. The risk assessment drives the policies, controls and procedures, which senior management approves. The policies set the depth of customer due diligence for each customer. Section 17D lets a reporting person rely on third parties to perform CDD, but it stays responsible for compliance. Customer due diligence feeds ongoing monitoring of the relationship, and every CDD result goes into records kept for at least seven years. CDD is triggered when a relationship starts, for occasional transactions of Rs 500,000 or more, for wire transfers, and for virtual asset service providers on occasional transactions of USD 1,000 or more; high-risk countries named by the Minister need the prescribed enhanced CDD.
Assess and document the risk
Under section 17, every reporting person must identify, assess and understand its money laundering, terrorism financing and proliferation financing risks for customers, countries or geographic areas, products, services, transactions and delivery channels. The assessment must reflect the nature and size of the business. It also has to consider reliance on third parties for parts of CDD, technological developments and the outcome of the national risk assessment.
Two practical rules follow. First, before launching a new product, business practice or new or developing technology, the reporting person must assess the risks it may bring and take measures to manage them. That includes any AI tooling you add to monitoring or case work. Second, the assessment must be documented in writing, kept up to date and made available to competent authorities without delay on request. The 2026 amendment lets a supervisory authority decide that its sector need not document assessments, but only where the sector's specific risks are clearly identified and understood. Unless your supervisor has told you so in writing, document it.
Set policies that senior management approves
Section 17A requires policies, controls and procedures that mitigate and manage the risks the assessment found. They must be proportionate to the size and nature of the business and approved by senior management. The reporting person has to monitor how they work, review and update them, and keep a written record of the policies, every change made after a review, and the steps taken to communicate them internally.
That last record is easy to overlook. If a policy changed after a review, an examiner may ask when it changed, why, who approved it and how staff were told.
Apply CDD and identify beneficial owners
Section 17C requires CDD when a business relationship starts, for occasional transactions of Rs 500,000 or more (single or linked), for domestic or cross-border wire transfers, when there are doubts about earlier identification data and whenever money laundering or terrorism financing is suspected. Virtual asset service providers apply CDD to occasional transactions of USD 1,000 or more. Where the customer isn't physically present, CDD can use a reliable and independent digital identification system.
Where risks are higher, the reporting person must apply enhanced due diligence that matches the risks identified. Where risks are lower it may simplify, unless there is a suspicion, in which case enhanced measures apply. Under section 17E, CDD also applies to existing customers at appropriate times, based on materiality and risk.
For a legal person, the beneficial owner is the natural person who ultimately owns or controls the customer, or on whose behalf a transaction is conducted. For a trust, the Act names the settlor, the trustee, any protector, each beneficiary or class of beneficiaries, and any other natural person exercising ultimate effective control. Layered global business structures are where this gets hard. The file should show each layer of the ownership chain, the source used to verify it and who approved any gap.
Rely on third parties without handing over responsibility
Section 17D lets a reporting person rely on third parties to perform CDD, subject to prescribed terms. It also says that a reporting person relying on a third party remains responsible for compliance with the Act. That sentence matters for any global business company that uses its management company to collect CDD.
Keep records for seven years
Section 17F sets three retention periods:
- CDD records, account files, business correspondence and identity documents for customers and beneficial owners, along with the results of any analysis, for at least seven years after the business relationship ends.
- Transaction records detailed enough to reconstruct each individual transaction, for seven years after the transaction completes.
- Copies of every STR and other report made to the FIU, with supporting documents, for at least seven years from the date of the report.
Retained isn't the same as retrievable. A file split across inboxes, vendor portals and unindexed drives may exist and still fail an urgent supervisory request.
Treat high-risk countries as a prescribed category
Under section 17H, the Minister may identify a jurisdiction that the FATF has flagged for strategic deficiencies as a high-risk country. Reporting persons must then apply the prescribed enhanced CDD to relationships and transactions involving it, and may need extra measures such as more reporting or limits on business. The FIU disseminates these designations, so your screening and risk rating rules need a way to absorb them quickly.
Register with the FIU
Section 14C requires every reporting person to register with the FIU. The FIU's registration page explains that the Financial Intelligence and Anti-Money Laundering (Registration of Reporting Persons) Regulations 2019 set out the framework, and that failure to register is an offence under regulation 7 of those Regulations. The Bank of Mauritius guideline adds that financial institutions register through their MLROs.
How does suspicious transaction reporting work in Mauritius?
Section 14(1) of FIAMLA requires every reporting person or auditor to report a suspicious transaction to the FIU promptly, and not later than five working days after the suspicion arose. Reports go to the FIU electronically through the goAML web platform. Under section 14(3), a reporting person who knew, or ought reasonably to have known, of a suspicious transaction and fails to report it within that period commits an offence. The penalty is a fine of up to one million rupees and imprisonment of up to five years.
- An employee who suspects money laundering makes an internal disclosure to the MLRO. The MLRO assesses it against all the other relevant information the institution holds. If the MLRO knows or has reason to believe the matter may be suspicious, the MLRO files an STR with the FIU through goAML within five working days of the suspicion arising. Regulation 30 requires separate registers of internal disclosures and external disclosures. Section 15 lists what each report contains, including the parties, the amount and circumstances, and the officers who dealt with the transaction. Failing to report is an offence with a fine of up to one million rupees and up to five years' imprisonment, and tipping off carries a fine of up to five million rupees and up to ten years. For each STR keep the date the suspicion arose, the facts available to the MLRO, the MLRO's decision and reasons, and the goAML reference and date sent.
FIAMLA defines a suspicious transaction broadly. It covers a transaction that gives reasonable suspicion of money laundering, proceeds of crime or terrorism or proliferation financing. It also covers a transaction made in circumstances of unusual or unjustified complexity, one with no apparent economic justification or lawful objective, or one made by or for a person whose identity hasn't been established.
The route inside the institution comes from the FIAML Regulations 2018, as the Bank of Mauritius guideline explains. An employee who suspects money laundering makes an internal disclosure to the MLRO. The MLRO assesses the internal disclosure against all the other relevant information the institution holds. If the MLRO knows or has reason to believe the matter may be suspicious, the MLRO files an STR with the FIU through goAML within five working days of the suspicion arising. Regulation 30 then requires separate registers of internal disclosures and external disclosures.
Section 15 lists what each report must contain:
- the parties to the transaction;
- the amount, the nature of the transaction and all the circumstances giving rise to the suspicion;
- the suspect's business relationship with the reporting person;
- where the suspect is an insider, whether they are still affiliated;
- any voluntary statement on the origin, source or destination of the proceeds;
- the impact on the financial soundness of the institution;
- the names of the officers, employees or agents who dealt with the transaction.
Most of that list is facts the investigator has already gathered. If the case file is complete when it reaches the MLRO, the five-day period goes on the decision, not on reassembling evidence.
Key insight: in Mauritius the five working days run from when the suspicion arose, not from when the MLRO opened the file. An MLRO who can show the date of each internal disclosure, the written assessment and the goAML submission date has the answer to the first question an examiner asks.
Two protections and one prohibition sit around the report. Section 16 protects anyone who reports a suspicion in good faith, whether or not it proves well founded. It also prohibits disclosing that an STR is being or has been filed, or that related information was requested by or supplied to the FIU. Breaching that tipping-off rule carries a fine of up to five million rupees and imprisonment of up to ten years.
For each STR, keep a record of:
- the event that prompted concern and the date the suspicion arose;
- the facts available to the MLRO at that point;
- the checks completed and any information still missing;
- the MLRO's decision and reasons, including decisions not to report;
- the goAML submission reference and the date it was sent;
- the controls applied afterward, without tipping off the customer.
What does the MLRO decide?
The MLRO decides whether an internal disclosure becomes an STR. The Bank of Mauritius guideline says it is incumbent on the MLRO, on behalf of the financial institution, to make suspicious transaction reports to the FIU.
- A financial institution must appoint an MLRO to receive internal reports and a Deputy MLRO who performs the MLRO's duties when the MLRO is absent. The MLRO has a right of direct access to the board of directors. A compliance officer at senior management level implements the AML/CFT program and keeps it compliant; the guideline says it is advisable for that to be a different person from the MLRO. A model or an AI agent can assemble the chronology, pull the ownership file and draft the report, and a complete case file lets the MLRO spend the five working days on the decision. It is incumbent on the MLRO, on behalf of the financial institution, to make suspicious transaction reports to the FIU. The MLRO and Deputy MLRO must be sufficiently senior, independent of customer-facing roles, have access to the systems and records needed to investigate, and be known to every employee.
Regulation 26 of the FIAML Regulations 2018 shapes the role. A financial institution must appoint an MLRO to receive internal reports and a Deputy MLRO who performs the MLRO's duties when the MLRO is absent. Both must be sufficiently senior or have sufficient experience and authority. The MLRO has a right of direct access to the board of directors, and both need the time and resources to do the job. The guideline adds that the MLRO and Deputy MLRO must be independent, particularly from customer-facing and business development roles.
The guideline treats the compliance officer as a separate role. Regulation 22 requires a compliance officer at senior management level who is responsible for implementing the AML/CFT program and keeping it compliant. The guideline says it is advisable for the compliance officer and the MLRO to be different people, but each institution may decide whether one person holds both. It also expects institutions to give the MLRO access to the systems and records needed to investigate, and to tell every employee who the MLRO and Deputy MLRO are.
None of this can be delegated to software. A model or an AI agent can assemble the chronology, pull the ownership file and draft the report. The judgment that there are reasonable grounds for suspicion, and the decision to file or not, stay with the MLRO.
What applies to banks supervised by the Bank of Mauritius?
Banks follow FIAMLA, the FIAML Regulations 2018 and the Banking Act 2004. Part VIIIA of the Banking Act, sections 64A to 64D, requires every financial institution and licence holder, including branches and subsidiaries, to run programs against money laundering and terrorism financing. Under section 64A(1)(b) and Regulation 22, those programs must match the institution's risks and size. At a minimum they include a senior compliance officer, staff screening at hiring, ongoing training and an independent audit function.
The Bank of Mauritius guideline sets out how the Bank expects those duties to work. It covers the risk-based approach, internal controls, CDD and enhanced due diligence, ongoing monitoring, sanctions and proliferation financing, suspicious transaction reporting, record keeping and training. The hosted guideline is dated January 2020, so it predates the 2026 amendments to FIAMLA. Where the two differ, follow the Act and ask the Bank or your counsel how it reads the change.
A bank should be able to show one evidence index that links policy to operation:
| Control area | Evidence to prepare | Warning sign |
|---|---|---|
| Business risk assessment | method, data, senior management approval, update history | assessment that does not mention proliferation financing |
| Policies and controls | approved versions, review record, staff communication | no record of when or why a policy changed |
| CDD and beneficial ownership | source records, verification results, exceptions | ownership chain with an unexplained layer |
| Enhanced due diligence | trigger, extra checks, approver | the same checklist for every higher-risk customer |
| Ongoing monitoring | scenarios, thresholds, alert evidence, tuning tests | alerts closed without supporting facts |
| Internal and external disclosures | separate registers, MLRO reasons, goAML references | no date for when the suspicion arose |
| Sanctions screening | list sources, screening triggers, match decisions | no rescreen after a list update or ownership change |
| Records | retention schedule, retrieval tests | records kept but not retrievable within days |
| Training and audit | role-based content, attendance, audit findings and closure | repeat findings without a named owner |
What applies to global business companies and management companies?
Global business sits with the FSC. According to the FSC's global business page, an applicant for a Global Business Licence must be a resident corporation conducting business outside Mauritius. A management company channels each Global Business Licence application to the FSC. The FSC licenses the management company under section 77 of the Financial Services Act 2007 to set up and manage global business corporations and provide nominee and trustee services. Before licensing a non-bank financial institution, the FSC checks that the applicant has compliance functions, internal controls and measures to prevent money laundering.
- A management company channels each Global Business Licence application to the FSC, and the FSC licenses the management company under section 77 of the Financial Services Act 2007 to set up and manage global business corporations and provide nominee and trustee services. Where the global business company is the reporting person and relies on its management company for CDD, the company remains responsible for compliance under section 17D. The global business company must be able to retrieve the underlying evidence from the management company, not just a confirmation that checks were done. A scope memo for each entity answers which licences it holds and which activities it performs, whether it is a reporting person and which supervisor covers it, who performs CDD, screening, monitoring and escalation, who the MLRO is and who files with the FIU, and how quickly it can produce the full customer and transaction file.
The FSC AML/CFT Handbook helps financial institutions under the FSC's purview comply with FIAMLA and the FIAML Regulations 2018. It is updated from time to time, so check that you are working from the current version.
The harder question is responsibility. A global business company, its management company and any group function may each touch CDD, monitoring and reporting. FIAMLA doesn't let that spread blur accountability. Where the company is the reporting person and relies on its management company for CDD, the company remains responsible for compliance under section 17D. The global business company must be able to retrieve the underlying evidence from the management company, not just a confirmation that checks were done.
Start with a short scope memo for each entity that answers:
- Which licences does the entity hold, and which activities does it actually perform?
- Is the entity a reporting person for each activity, and which supervisor covers it?
- Who performs CDD, screening, monitoring and escalation: the entity, the management company, a group team or another provider?
- Who is the MLRO, and who files with the FIU?
- How quickly can the entity produce the full customer and transaction file?
Group policies can set a common minimum, but the Mauritian entity still needs local owners, a local filing route and a record of any Mauritian rule that is stricter than the group standard. Where group and local rules conflict, get legal advice and, if needed, ask the supervisor.
- FIAMLA was amended by Act No. 3 of 2026 from April 18, 2026: risk assessments must now cover proliferation financing, and the beneficial owner definition was replaced.
- Suspicious transactions go to the FIU through goAML promptly and within five working days of the suspicion arising; failing to report is an offence.
- The Bank of Mauritius supervises banks and other Banking Act licensees; the FSC supervises non-bank financial services licensees and global business companies.
- A reporting person that relies on a management company or other third party for CDD stays responsible for compliance under section 17D.
- The MLRO assesses internal disclosures and files STRs on behalf of the institution; that decision cannot be handed to software.
Conclusion
A Mauritius AML/CFT program is judged as a chain. The documented risk assessment, which now has to cover proliferation financing and take account of the Second National Risk Assessment, drives the policies senior management approves. The policies set the depth of CDD and beneficial ownership work. Monitoring and staff disclosures reach the MLRO, who decides what goes to the FIU within five working days. The records let a supervisor rebuild each step for seven years. With the next ESAAMLG evaluation scheduled for 2028, supervisors will look for evidence that this chain works in practice.
For the wider program elements an examiner tests, see our AML compliance guide, and use the AML program charter template to set out board, management, compliance officer and MLRO roles. The FluxForce jurisdiction library covers other markets your group may operate in. If you want agents to draft STRs while your MLRO approves every filing, see our regulatory reporting page.
Request a Mauritius AML/CFT program walkthrough
Frequently Asked Questions
About the author
Sahil Kataria
Founder and CEO of FluxForce
Share this article