

Listen To Our Podcast🎧
Why does adverse media need a control framework?
Running adverse media screening is one thing. Explaining to an examiner why it is set up the way it is takes more. Which customers are screened, and how often? Which crimes count? Does an allegation raise an alert, or only a charge? Which sources are trusted, and who decided? When an analyst cleared a hit last March, where is the reasoning? If the answers live in a vendor's default settings and in analysts' heads, you have a screening tool. You don't yet have a control.
The difference matters because adverse media is harder to pin down than the other screening controls. The Wolfsberg Group describes sanctions and PEP screening as traditionally list-based. Adverse media starts from the open press, court records and regulatory notices, where names are inconsistent, stories change, and much of what turns up is about someone else. A control framework is what turns that material into decisions you can defend.
This guide is for MLROs and heads of compliance at banks, payment firms, fintechs and other regulated firms. It sets out what the FATF standard, the EBA risk factor guidelines, the FCA Financial Crime Guide, the EU AML Regulation and the US bank program rule say about adverse information, and what the Wolfsberg Group's negative news screening FAQs add. It then builds an eight-part control framework, from scope to quality assurance, and covers what to look for in adverse media screening software. It reflects those texts as they stood on October 20, 2026. It isn't legal advice, and the rules that apply to you depend on your jurisdiction and licence type.
- Where the expectation to screen adverse media comes from under the FATF standard and EU, UK and US rules.
- The eight parts of an adverse media control framework, and the decision each one records.
- How to set scope, risk categories, risk stages and sources, and how to judge whether a source is credible.
- How to discount alerts, decide materiality and record the reasoning so it survives a file review.
- What adverse media screening software should do, where AI agents fit, and which decisions stay with people.
Request the adverse-media monitoring control matrix and a shadow-mode run
Adverse media monitoring is a risk-based control, not a fixed rule. The FATF standard expects ongoing due diligence, and the EBA and the FCA name the customer's reputation and credible allegations as part of the risk picture. A defensible framework writes down eight decisions: scope, risk categories, risk stages, sources, matching and discounting, materiality and escalation, the decision record, and quality assurance with management information.
What is adverse media monitoring, and where does the obligation come from?
Adverse media, also called negative news, is public information that suggests a customer or a related person may be involved in financial crime. The Wolfsberg Group's FAQs on negative news screening recognise that there is no universally agreed and accepted definition of Negative News. For its FAQs, the Group uses a broad working definition: information available in the public domain which FIs would consider relevant to the management of Financial Crime risk. Its footnote lists what public domain covers in practice: media sources from online news outlets, court records, regulatory disclosures, penalty notices.
Adverse media screening is the act of checking names against that information. Adverse media monitoring is the same check repeated through the life of the relationship, so that news which appears after onboarding still reaches the file. If you want a short definition to share with your team, our glossary entry on adverse media screening covers the basics.
No single rule tells you to "run adverse media screening". The expectation comes from the duty to understand customer risk and keep that understanding current. The FATF Recommendations require firms to conduct ongoing due diligence on the business relationship and scrutiny of transactions undertaken throughout the course of that relationship to ensure that the transactions being conducted are consistent with the institution's knowledge of the customer, their business and risk profile. Among the enhanced measures the interpretive note gives for higher-risk relationships is obtaining additional information on the customer (e.g. occupation, volume of assets, information available through public databases, internet, etc.). The Wolfsberg FAQs make the same point about FATF's wording: although FATF does not explicitly refer to negative news screening, reference to conducting "adverse media searches" can be found in its Risk-Based Approach Guidance under enhanced due diligence measures.
The EBA risk factor guidelines are more direct. When identifying customer risk, firms should consider the risk related to the customer's and the customer's beneficial owner's reputation. The guidelines then ask whether there are adverse media reports or other relevant sources of information about the customer, for example are there any allegations of criminality or terrorism against the customer or the beneficial owner. Among the sources firms should consider, they list information from credible and reliable open sources, such as reports in reputable newspapers. In their list of EDD measures, they give adverse media searches as an example of information about the customer's or beneficial owner's reputation.
In the UK, the FCA's Financial Crime Guide, FCG 3.2, lists among its examples of EDD gaining a better understanding of the customer's or beneficial owner's reputation and/or role in public life and assessing how this affects the level of risk associated with the business relationship. In its table of poor practice, it includes a firm that disregards allegations of the customer's or beneficial owner's criminal activity from reputable sources repeated over a sustained period of time.
In the EU, the AML Regulation (EU) 2024/1624 will set the rules directly from 10 July 2027. Article 26 requires ongoing monitoring of business relationships, and it requires firms to review and, where relevant, update customer information where there is a change in the relevant circumstances of a customer or where they become aware of a relevant fact which pertains to the customer. Article 76 sets the conditions for processing personal data relating to criminal convictions and offences. Adverse media about alleged financial crime often falls into that category, and those conditions shape the framework below.
In the US, the bank program rule, 31 CFR 1020.210, requires appropriate risk-based procedures for conducting ongoing customer due diligence, including conducting ongoing monitoring to identify and report suspicious transactions and, on a risk basis, to maintain and update customer information. That rule doesn't use the term adverse media. Whether and how you screen news is a decision your own risk-based procedures have to make and justify.
| Source | What it says about adverse information | Type |
|---|---|---|
| FATF Recommendation 10 and its interpretive note | Ongoing due diligence; public databases and the internet as an example of enhanced information | International standard |
| EBA ML/TF Risk Factors Guidelines (EBA/GL/2021/02) | Reputation as a customer risk factor; adverse media reports and the credibility of allegations; reputable newspapers as a source | EU supervisory guidelines |
| FCA Financial Crime Guide, FCG 3.2 | Reputation in EDD; disregarding repeated allegations from reputable sources is poor practice | UK regulatory guidance |
| EU AML Regulation 2024/1624 (from 10 July 2027) | Ongoing monitoring and review on a change in circumstances or a relevant fact; conditions for processing criminal offence data | EU regulation |
| 31 CFR 1020.210 | Risk-based ongoing CDD and updating customer information; no adverse media term | US rule |
| Wolfsberg Group NNS FAQs (2022) | How to design scope, sources, alert handling, quality assurance and management information | Industry guidance |
What does an adverse media control framework need to cover?
The Wolfsberg FAQs say plainly that there is no single, universally agreed approach to NNS. They also say it is important to acknowledge that NNS should not be a zero-tolerance process and that FIs may conclude that NNS is not necessary in all circumstances. That leaves the design to you, which is exactly why the design has to be written down. An examiner can't test a setting nobody chose.
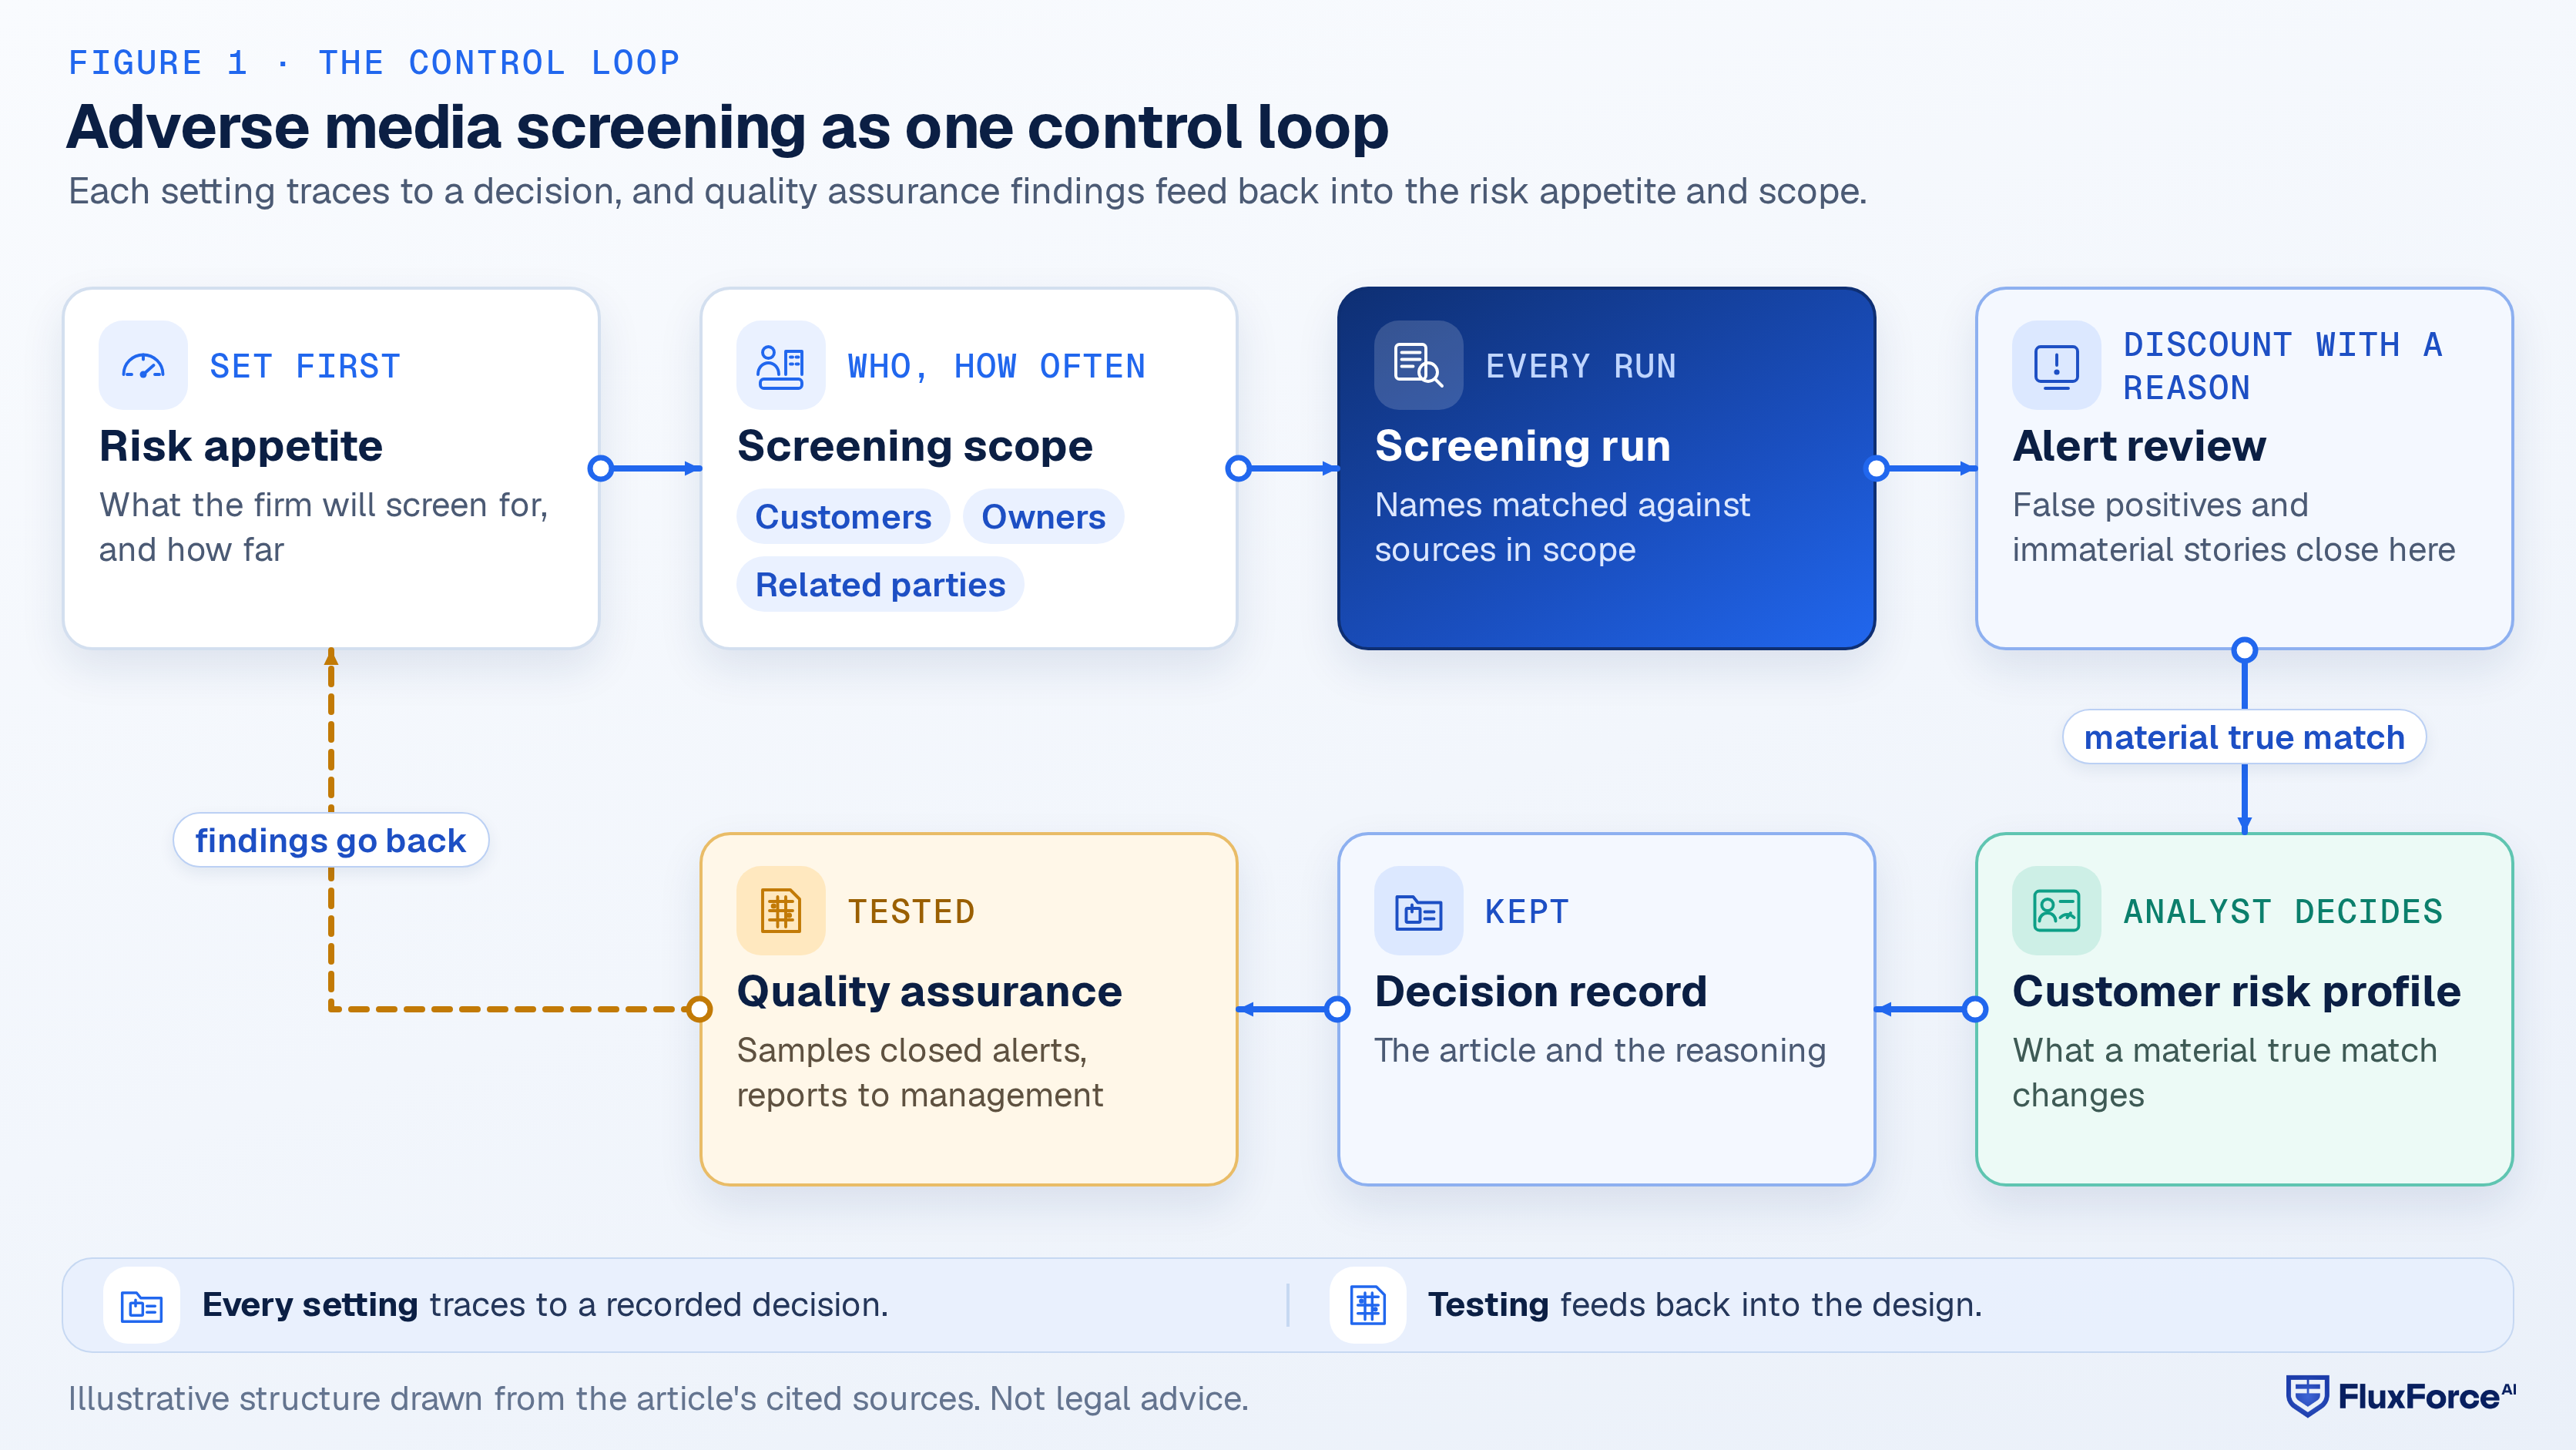
- The risk appetite sets the screening scope, meaning which customers, owners and related parties are screened, how often and against which sources. The screening scope drives each screening run, which matches names against the sources and risk categories in scope. Each screening run produces alerts for alert review, where false positives and immaterial stories are discounted with a reason. A material true match leaves alert review and goes to the customer risk profile, where an analyst decides what it changes. The customer risk profile change, or the decision not to change it, is written to the decision record with the article and the reasoning. The decision record feeds quality assurance, which samples closed alerts and reports results to management. Quality assurance findings go back to the risk appetite and scope.
The framework below is our reading of the sources in this guide. It turns the Wolfsberg list of risk-based decisions into eight controls, each with an owner and a record.
| Control | Decision it records | Owner |
|---|---|---|
| 1. Scope | Which customers, beneficial owners and related parties are screened, at which points in the lifecycle and how often | MLRO, approved under the risk appetite |
| 2. Risk categories | Which offences count as adverse, and what is excluded | MLRO |
| 3. Risk stages | Whether allegations, investigations, charges or only convictions raise an alert | MLRO |
| 4. Sources | Which sources and languages are covered, and how their credibility is assessed | MLRO, with the vendor's evidence |
| 5. Matching and discounting | Which identifiers are compared and which alerts can be closed by rule | MLRO, tested by quality assurance |
| 6. Materiality and escalation | What makes a true match material, and who it goes to | Analyst, then MLRO |
| 7. Decision record | What every closed alert has to show | Analyst |
| 8. Quality assurance and MI | How closed alerts are sampled, how the false positive population is tested and what management sees | Quality assurance, reported to senior management |
The first figure shows how the controls connect. The risk appetite sets the screening scope, meaning which customers, owners and related parties are screened, how often and against which sources. The screening scope drives each screening run, which matches names against the sources and risk categories in scope. Each screening run produces alerts for alert review, where false positives and immaterial stories are discounted with a reason. A material true match leaves alert review and goes to the customer risk profile, where an analyst decides what it changes. The customer risk profile change, or the decision not to change it, is written to the decision record with the article and the reasoning. The decision record feeds quality assurance, which samples closed alerts and reports results to management. Quality assurance findings go back to the risk appetite and scope, so the framework is tuned instead of being left as it was configured on day one.
Two things follow from this design. Every setting in the screening tool should trace back to a decision in one of the eight controls, with a date and an owner. The record of each closed alert should also be good enough that someone who wasn't there can see what was found, why it was or wasn't about the customer, and why it did or didn't matter.
Who and what should be in scope?
Scope is the first decision, and it shouldn't be the same for every customer. The Wolfsberg FAQs tie the value of screening to how much is published about a person: customer types such as High Net Worth individuals, PEPs and Institutional customers (Large Corporates and FIs), are more likely to have a high public profile. For those customers, broad-based screening of both structured and unstructured sources may be appropriate on a risk sensitive basis. For a typical retail customer, more targeted searches of structured news and media sources might be more appropriate to ensure an effective use of resources. The FAQs go further: it may also be appropriate not to conduct NNS, and an FI would not be expected to devote resources to NNS where the added value is negligible or disproportionate to its Financial Crime Risks.
The scope decision should name four things:
- Who is screened. The FAQs note that FIs will typically focus NNS on customers and business relationships. The EBA guidelines put the beneficial owner alongside the customer for reputation risk, and the FCA lists carrying out searches on a corporate customer's directors or other individuals exercising control as an example of EDD.
- Which segments get which depth. The Wolfsberg FAQs suggest considering the products a customer uses, the segment to which the customer belongs, the geographies where the customer is based or to which they have a nexus and the status of the customer's internal risk rating or score.
- When screening runs. The FAQs give frequency options (daily, weekly, monthly, quarterly, annually) and stages including onboarding, triggered event, periodic and ongoing screening.
- How far back you look. A multi-year look-back threshold may be appropriate, and once an initial review has been conducted (e.g., at onboarding) it may only be necessary to screen against new media events.
Write the reasons down next to each choice. If retail customers get structured-source screening only, say why that fits your risk assessment. If you don't screen a segment at all, say what other control covers it. The Wolfsberg FAQs suggest considering whether alternative measures such as anti-fraud databases provide more effective means of risk identification.
Scope also changes over time. A customer whose risk rating rises should move into the deeper screening tier. This is where adverse media meets the rest of customer due diligence: our guide to customer due diligence controls covers review cycles by risk tier and how adverse media alerts can trigger an out-of-cycle review, and our answer on perpetual KYC explains how an event such as a news story can trigger a review between scheduled dates.
Which risk categories and stages should raise an alert?
The Wolfsberg FAQs name two settings to decide when establishing screening: the risk categories to screen e.g., the types of crime or event in scope of NNS, and the maturity or stage of the crime or event committed.
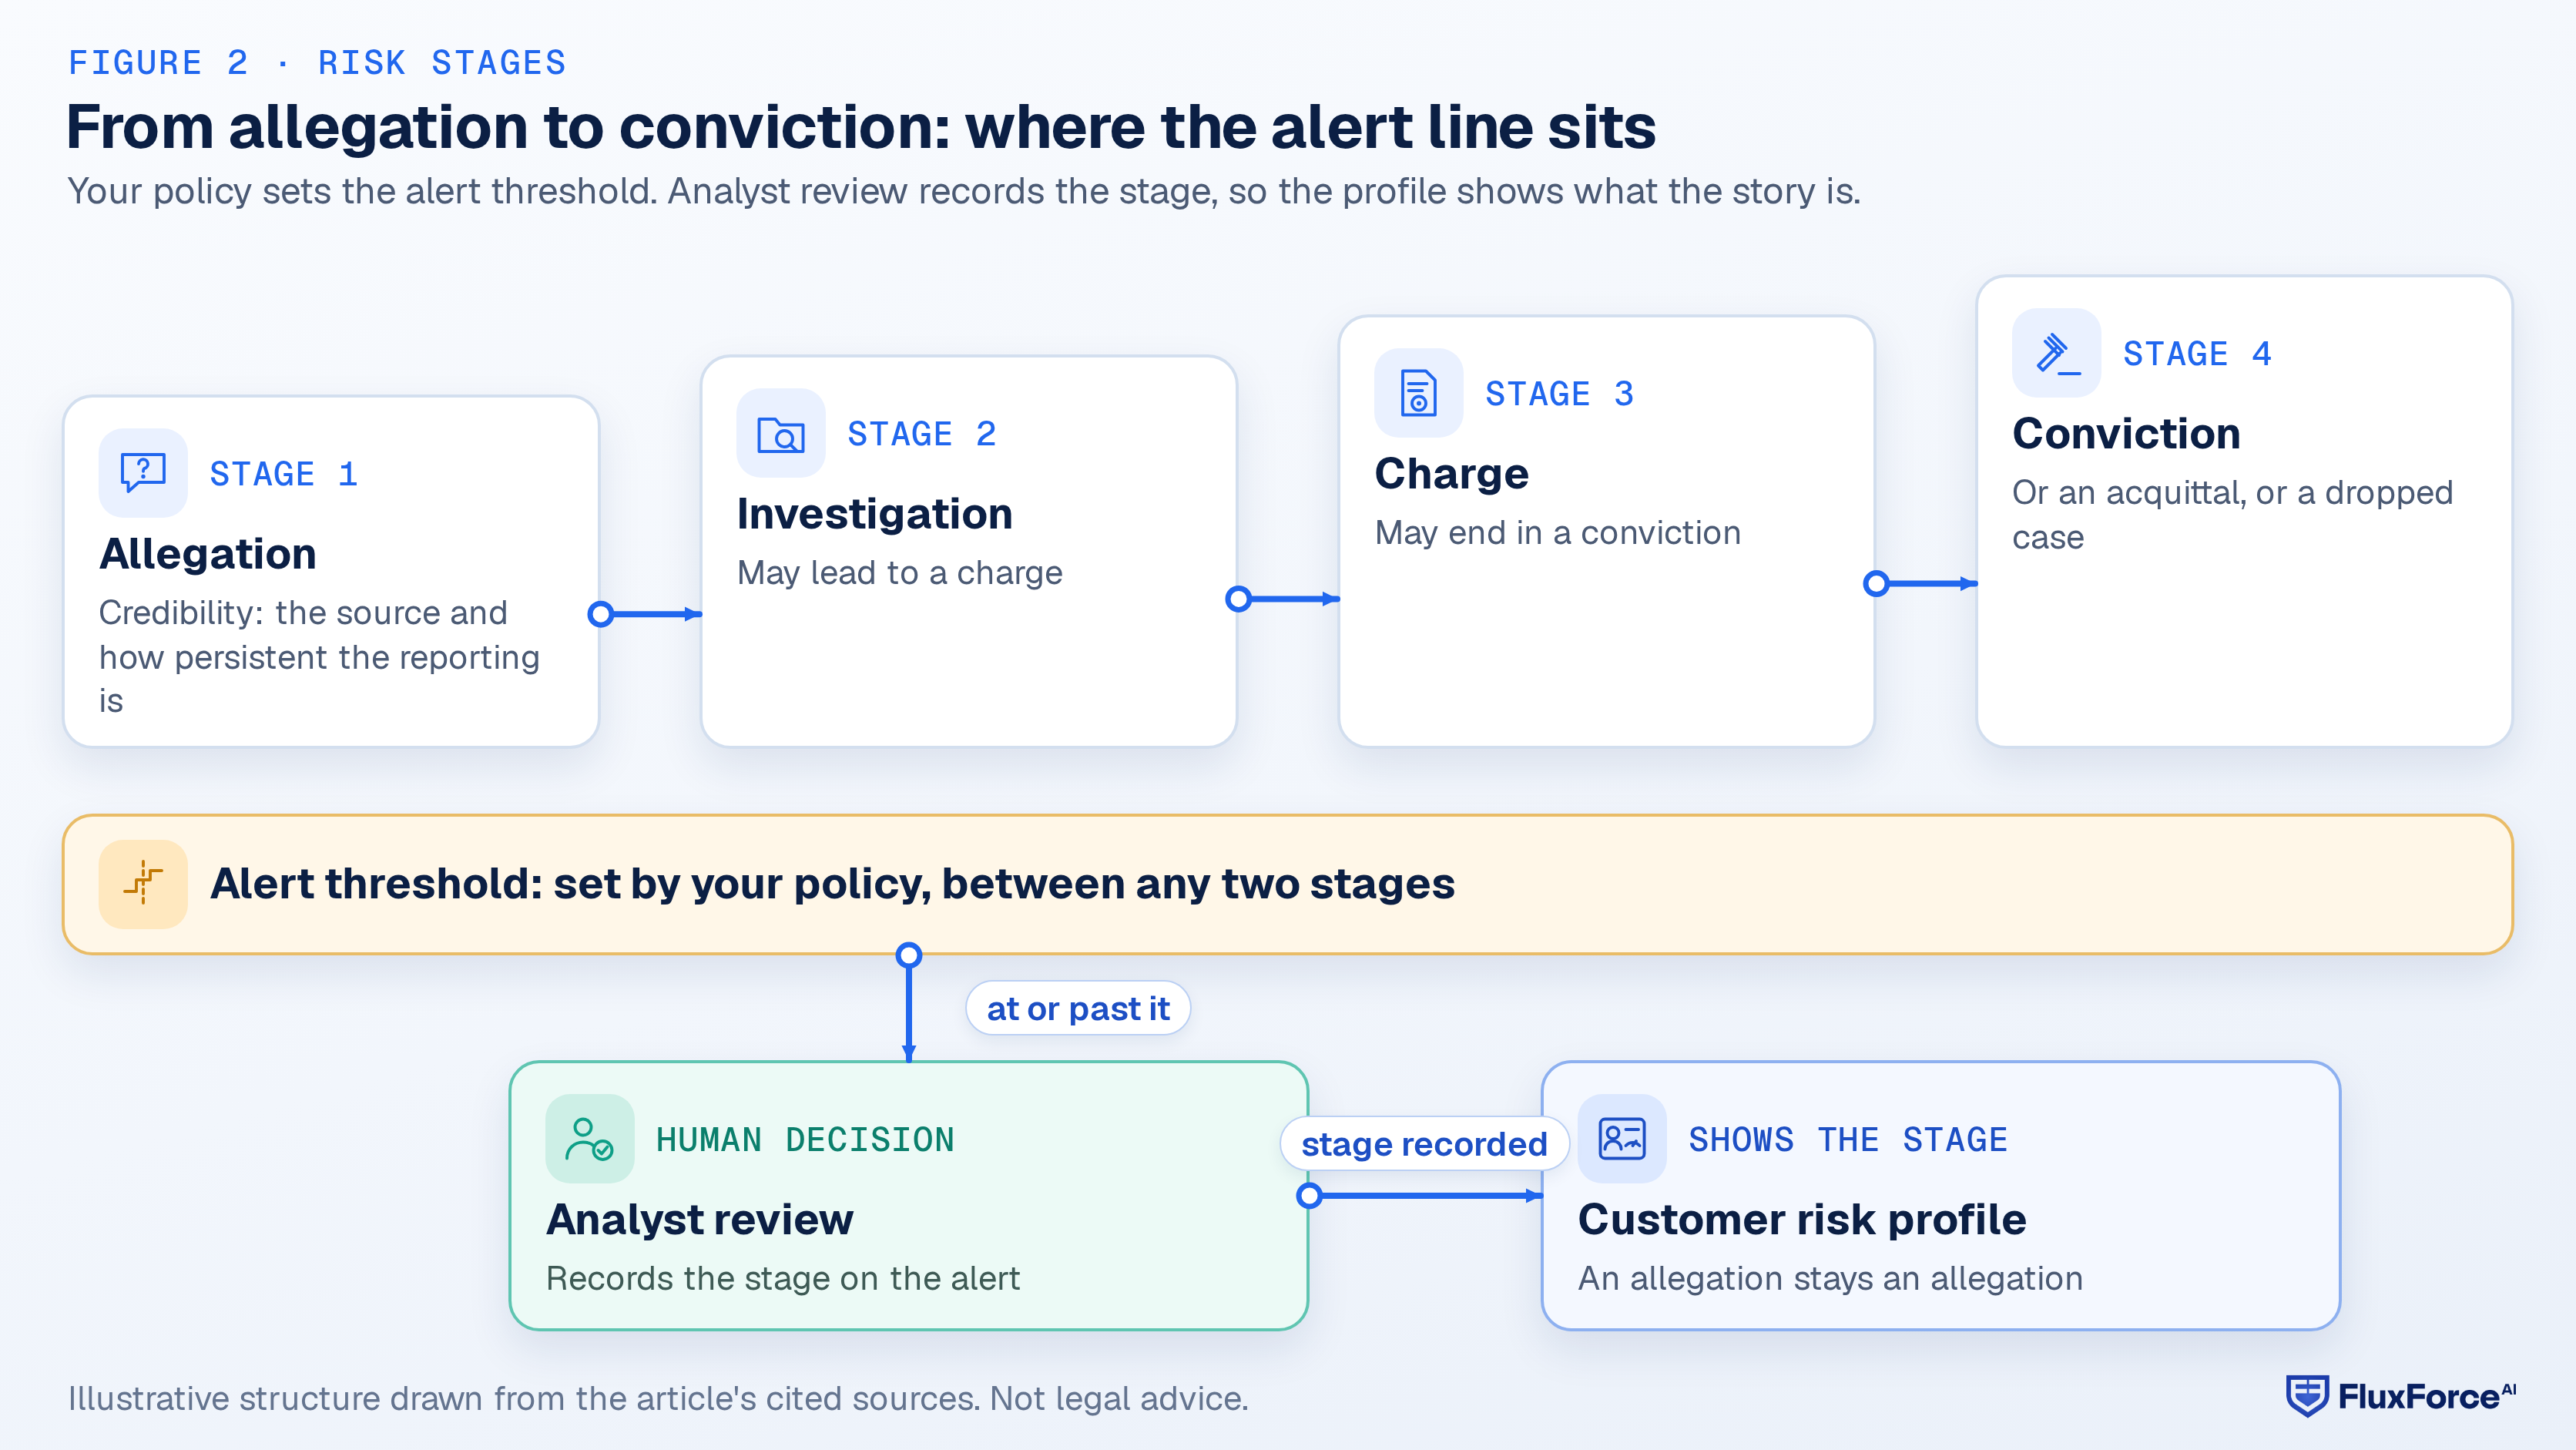
- An allegation may become an investigation, and the story's credibility depends on the source and how persistent the reporting is. An investigation may lead to a charge. A charge may end in a conviction, or in an acquittal or a dropped case. Stories at or past the alert threshold your policy sets go to analyst review, with the stage recorded on the alert. In analyst review, the stage the story has reached is recorded, so the customer risk profile shows an allegation as an allegation and a conviction as a conviction.
Risk categories are the offences you care about. The FAQs give examples such as Money Laundering, Terrorism/Terrorist Financing, Bribery and Corruption, Organised Crime, Drug Trafficking, Human Trafficking, Wildlife Trafficking, Proliferation and Proliferation Financing, and Tax Evasion. They also expect firms to exclude what isn't relevant, such as speeding fines and public disorder offences which are not related to Financial Crime. Your list should follow your own risk assessment. A trade finance business might add sanctions evasion and customs fraud, while a consumer payments firm might weight fraud and scams more heavily.
Risk stages are where the hard choice sits. The FAQs describe the path: the risk stage is the maturity of the offence and starts with an allegation, which then likely becomes an investigation which may lead to charges ending with a conviction. They also describe the trade-off: alert volumes at the allegation stage will be higher than receiving an alert at conviction stage once the alleged crime has been investigated and may have less AML/CTF value.
Waiting for convictions is tempting because it cuts volume. The sources in this guide argue against making it the only setting. The EBA guidelines say firms should determine the credibility of allegations on the basis of the quality and independence of the source of the data and the persistence of reporting of these allegations, among other considerations. They add a sentence worth putting in your policy: firms should note that the absence of criminal convictions alone may not be sufficient to dismiss allegations of wrongdoing. The FCA's poor-practice example, quoted above, is about allegations too: it refers to repeated allegations from reputable sources, not convictions.
A conviction-only alert line is a choice, not a default. If you make it, write down why, because the EBA says the absence of a conviction alone may not be enough to dismiss an allegation.
The EU AML Regulation adds conditions on how you handle what you find. Under Article 76, firms may process criminal offence data only where it relates to money laundering, its predicate offences or terrorist financing, where the data originate from reliable sources, are accurate and up-to-date, and where firms have procedures in place that allow the distinction, in the processing of such data, between allegations, investigations, proceedings and convictions, taking into account the fundamental right to a fair trial, the right of defence and the presumption of innocence. That is a record-keeping requirement as much as a screening one. An alert, a risk profile entry and a decision should each say which stage the story had reached.
The second figure shows the stages and where your policy sets the line. An allegation may become an investigation, and the story's credibility depends on the source and how persistent the reporting is. An investigation may lead to a charge. A charge may end in a conviction, or in an acquittal or a dropped case. Stories at or past the alert threshold your policy sets go to analyst review, with the stage recorded on the alert. In analyst review, the stage the story has reached is recorded, so the customer risk profile shows an allegation as an allegation and a conviction as a conviction.
A workable policy often sets different thresholds by category and segment. For example, you might alert on credible allegations of bribery or corruption for PEPs and high-risk corporates, and on charges or convictions for lower-risk retail customers. Whatever you choose, write down why, and test the result in quality assurance.
How do you judge whether a source is credible?
Source choice decides what your screening can find and how much of it is noise. The Wolfsberg FAQs treat the credibility of the media source as a deciding factor in whether it should be used, and say that factors such as the completeness, accuracy and coverage of the source should be considered. If you buy content from a vendor, the FAQs recommend that the FI understands the evaluation of reliability performed by the vendor and the controls they have in place to mitigate the risk of unreliable sources influencing the screening process.
The FAQs list what tends to mark a reputable source. These are the factors, in our words:
| Factor | Signs of a more reliable source | Signs of a less reliable source |
|---|---|---|
| Media type | International news agencies and national newspapers; regional outlets for local events | Content that can be edited by network participants |
| Content | Editorial oversight | Content corroborated only from social media, non-professional or opinion-based content |
| Geopolitical context | Politically neutral publications; independent press | Media controlled or influenced by leaders or leading parties; polarised reporting |
| Redundancy | The story is substantiated by other reputable sources | A single uncorroborated source |
| Editorial coherence | Specific details, original sources, citations and quotes | Errors, emotional language and eye-catching words |
Two points deserve a place in your source policy. The first is disinformation. The FAQs note that the risk that disinformation weakens the application of NNS may to some extent be mitigated through careful evaluation of sources. A single story from an unknown site shouldn't drive a relationship decision on its own. The EBA guidelines make a similar point about risk sources in general: firms should not normally rely on only one source to identify ML/TF risks. From July 2027, the EU rule that criminal offence data must originate from reliable sources gives the same point legal force for EU firms.
The second is local news. The FAQs note that regional and local news providers may report on events which are not covered by larger scale outlets. For customers in markets where the press writes in other scripts, they say there could be a need to screen the names of customers in the respective local language, and that the screening system needs to support non-Latin character sets. Where you can't cover a market's local press, record that gap and decide what compensates for it.
Can you rely on internet search engines?
If your team checks names with a search engine, the Wolfsberg FAQs don't rule it out, but they are cautious. While internet search engines may be used for certain aspects of NNS, it should be acknowledged that they have not been designed to assess Financial Crime Risk and may inadvertently de-prioritise information most relevant for this purpose. The FAQs also note that screening results may differ with each search, even with the same search phrase, depending on timing. Search engines filter out content to match individual browsing preferences, so results can vary greatly across different users.
If search engines are part of your process, three controls help:
- Fixed search strings. The FAQs say search strings should be agreed internally and aligned to each FI's risk appetite, and recommend keeping settings consistent to avoid inconsistencies in results or incorrectly applied search criteria.
- Saved evidence. Search engines, website owners or news purveyors have the right to purge, alter or archive the content at any time, so save a copy of any article you rely on, with the date you saw it.
- A documented limit. Record which customer segments manual search covers and which need a database or monitoring service instead.
How should matching, discounting and materiality work?
Each alert has to be closed or escalated, and each closure needs a reason you can defend. The Wolfsberg FAQs separate two reasons for closing an alert, and your procedures should too.
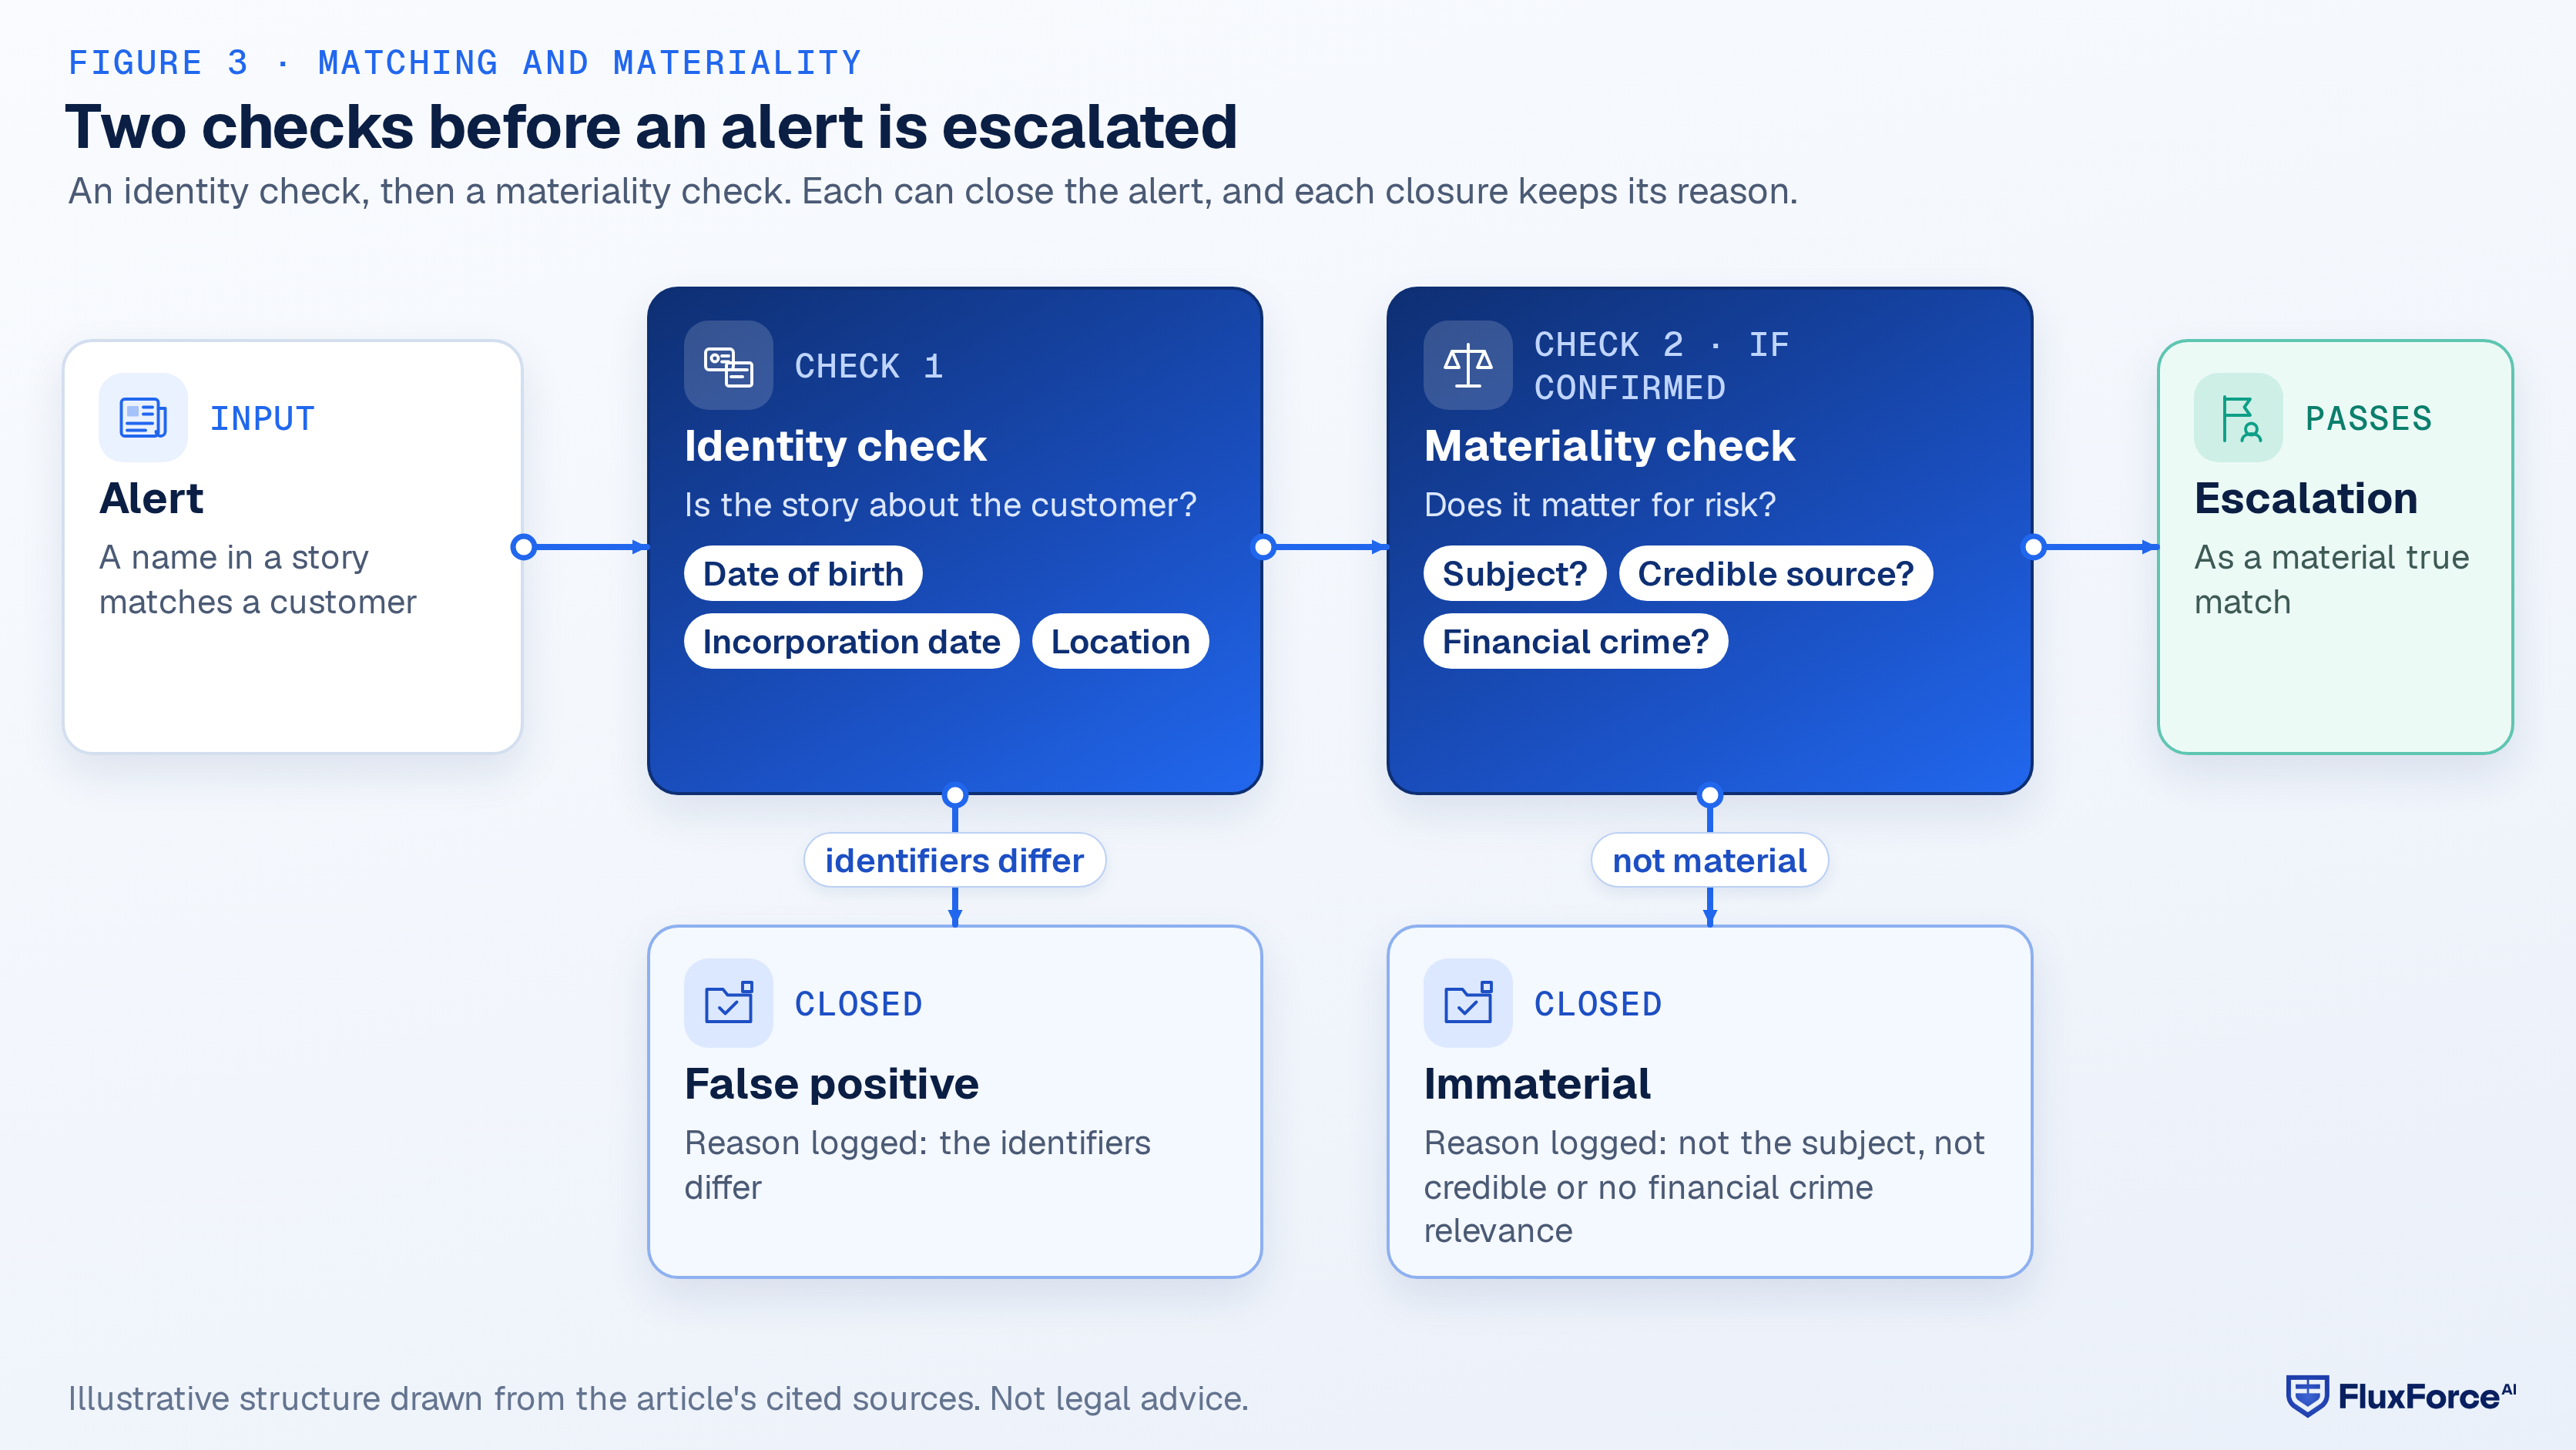
- Every alert goes first to an identity check: is the person or company in the story the customer? If identifiers such as date of birth, incorporation date or location differ, the identity check closes the alert as a false positive with the reason logged. If the identity check confirms the story is about the customer, the alert moves to a materiality check. The materiality check closes the alert as immaterial when the customer isn't the subject, the source isn't credible or the story has no financial crime relevance. A story that passes the materiality check goes to escalation as a material true match.
A false positive is a story about someone else. The FAQs give examples of discounting on this basis: a significant difference between the customer's name and the name that is the subject of the news article, and differences in secondary identifiers such as date of birth, date of incorporation or gender. They also allow weaker criteria, such as profession, residence and other situational factors which make a positive match unlikely.
An immaterial match is a story about the customer that doesn't matter for financial crime risk. The FAQs' examples include cases where the FI's customer is not the subject (e.g., customer is a plaintiff) and where the source of NNS is deemed not to be credible (e.g., blogs, tabloids).
The third figure shows the adjudication path. Every alert goes first to an identity check: is the person or company in the story the customer? If identifiers such as date of birth, incorporation date or location differ, the identity check closes the alert as a false positive with the reason logged. If the identity check confirms the story is about the customer, the alert moves to a materiality check. The materiality check closes the alert as immaterial when the customer isn't the subject, the source isn't credible or the story has no financial crime relevance. A story that passes the materiality check goes to escalation as a material true match.
Rules can close some alerts without a person. The FAQs describe auto discounting as the use of rules designed to manage common false positive alerts eliminating unnecessary manual review, and give the example of auto discounting any alerts where the customer's date of birth differs from the date of birth referenced in the media source by 1 year or more. They also describe a choice between a rules-based approach, which is a more prescriptive set of steps, and a risk-based approach that enables the use of additional parameters and judgment.
Automated discounting is a control in its own right, so treat it like one. The FAQs say that where technology is being used, it is important that FIs document all alert management solutions being used, the rationale for implementation and ensure that appropriate controls are in place to review periodically the performance of deployed applications. In practice, that means every auto-discount rule has a written rationale, an owner, an approval date and a test, and that quality assurance samples the alerts the rules closed as well as the ones people closed.
Materiality is the analyst's judgment, and it needs written guidance. The FAQs say procedures should cover alert materiality, so that while a false positive alert would be discounted, a positive match could be considered material where the nature of the information may indicate a heightened Financial Crime or Reputational Risk to the FI. For alerts that can't be resolved alone, procedures should give instructions on what further investigation is to be conducted, including input from other departments and teams.
What happens after a material true match?
A material true match is new information about the customer's risk. It isn't a decision. The Wolfsberg FAQs describe what it can lead to: revealing involvement in criminal activity which may determine the need for additional due diligence and/or targeted reviews of past transactional activity to inform the decision to on-board, maintain or exit a relationship. It can also inform the risk assessment and classification of the customer, and provide additional context to support an investigation into potentially suspicious activity.
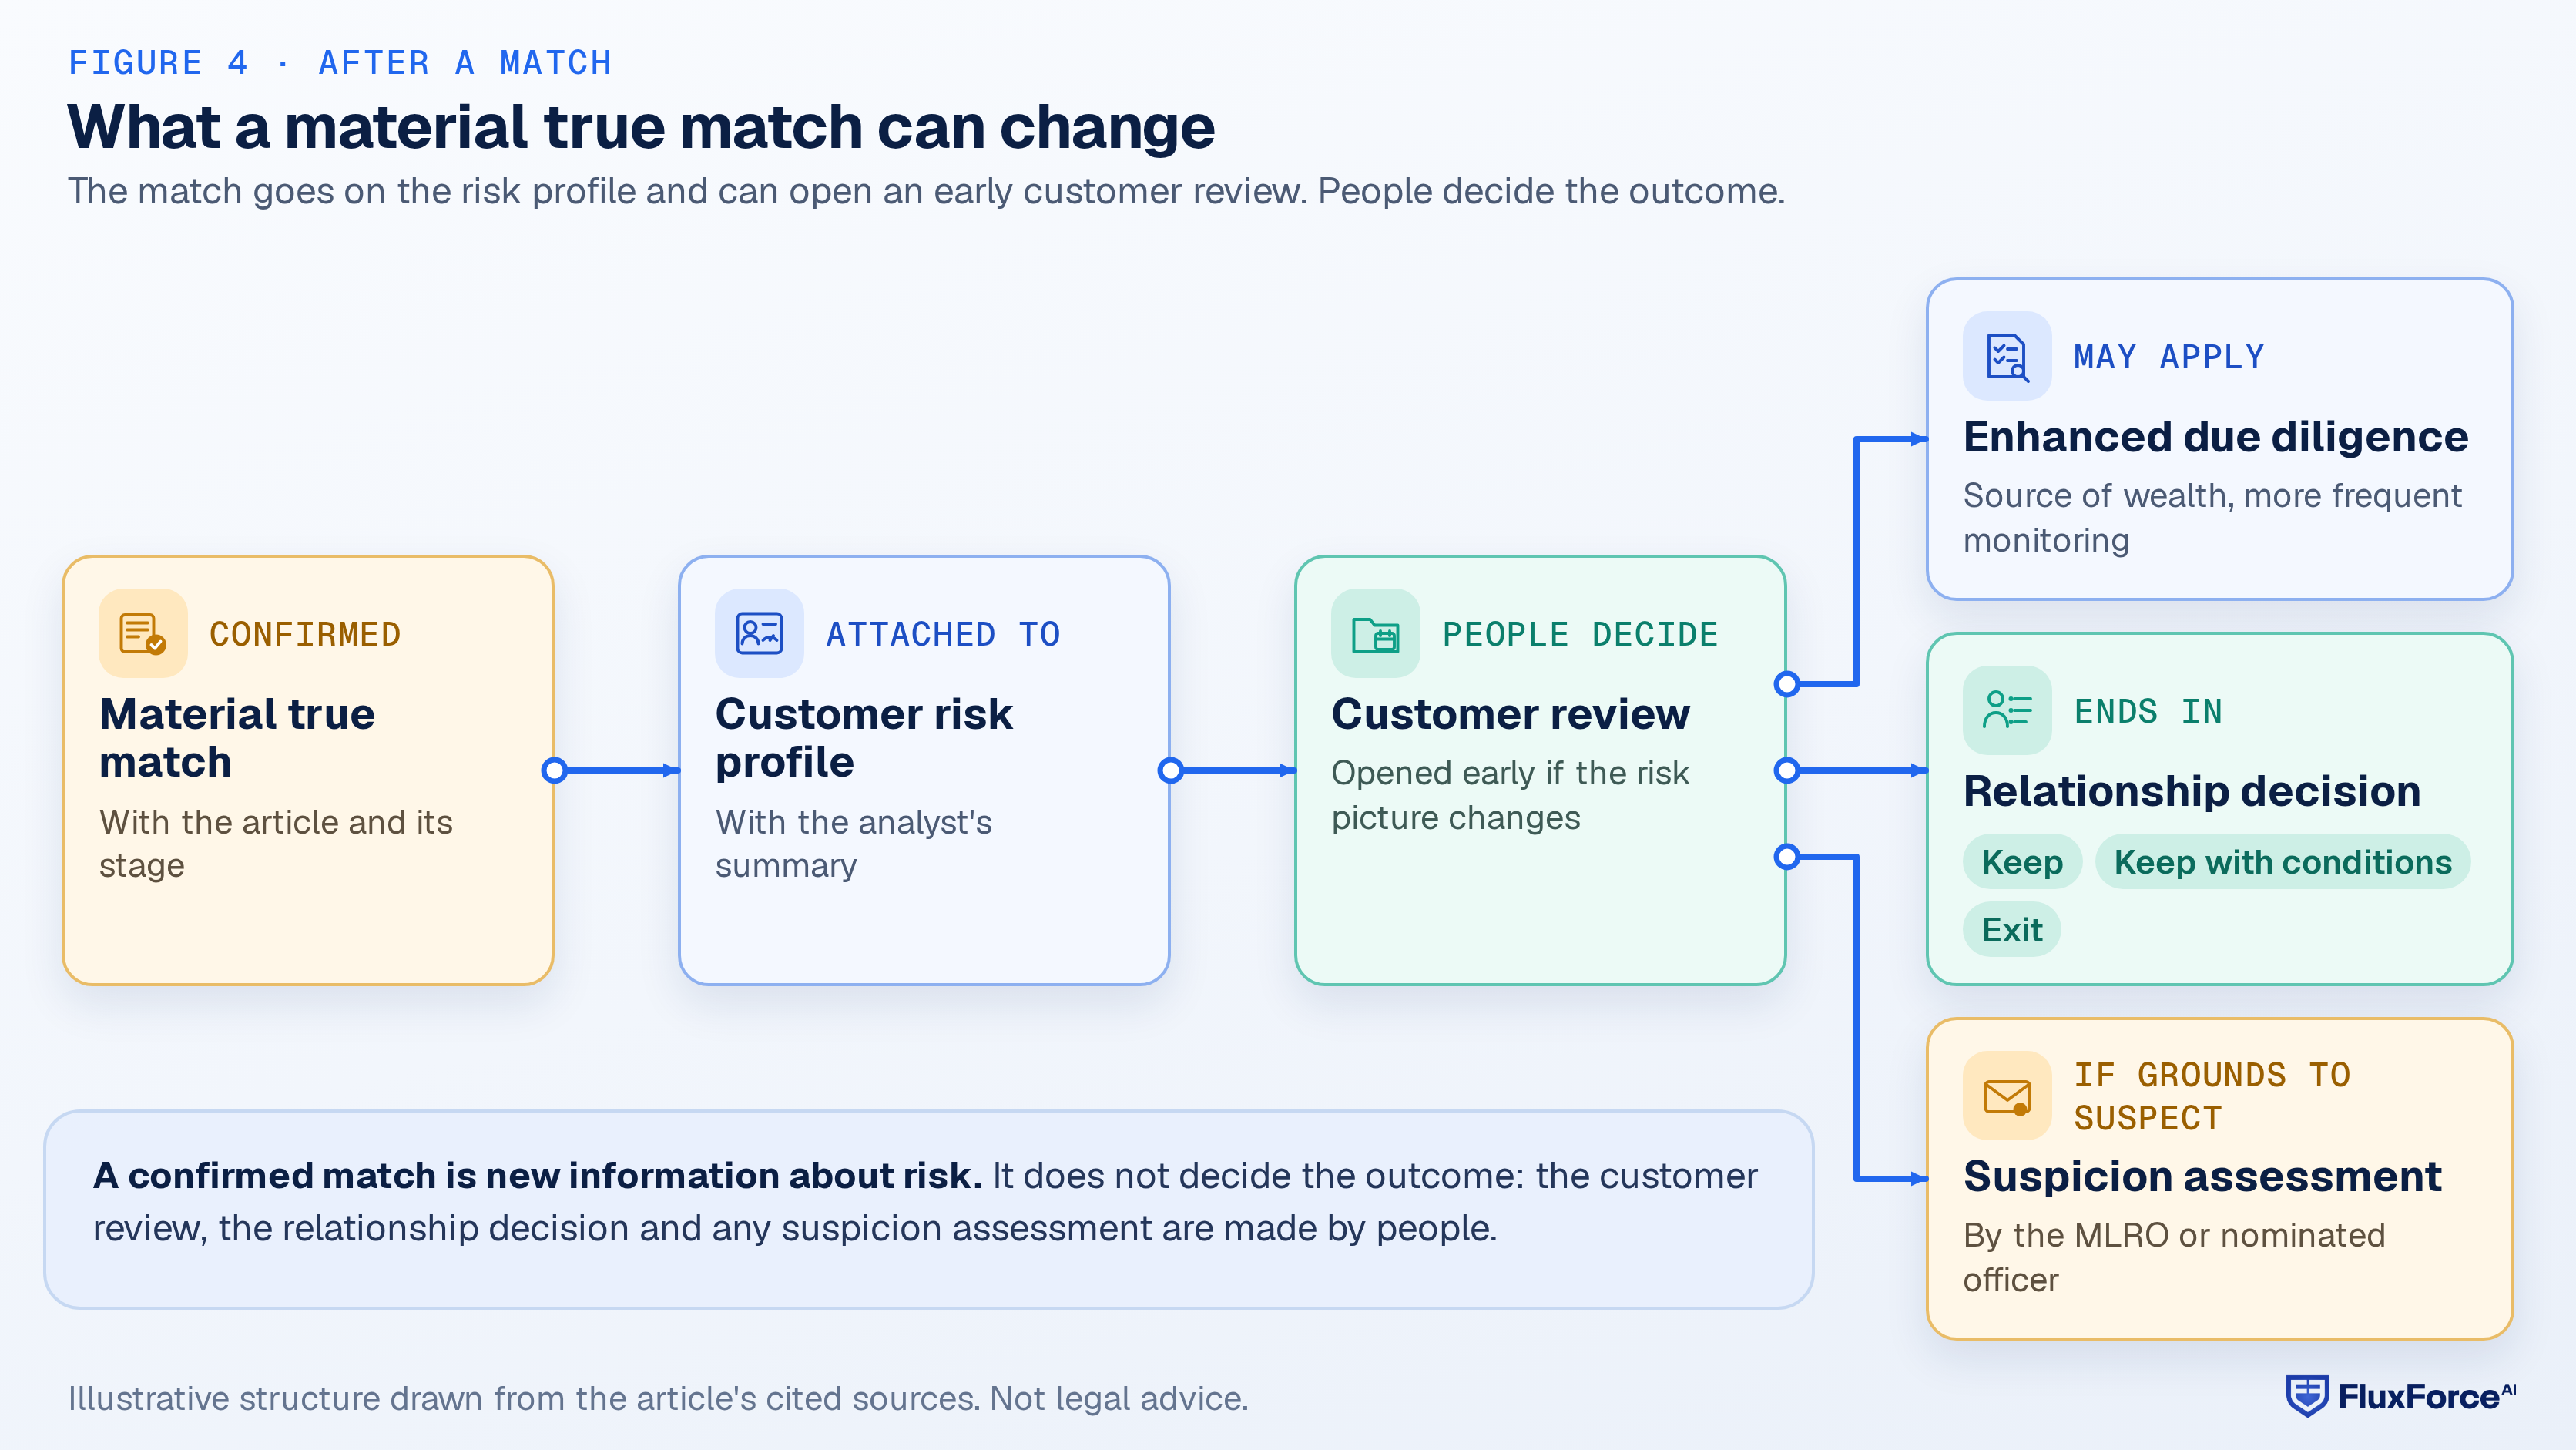
- A material true match is attached to the customer risk profile with the article, the stage and the analyst's summary. When the match changes the risk picture, the customer risk profile opens a customer review before the next scheduled date. The customer review may apply enhanced due diligence, such as source of wealth questions or more frequent monitoring. The customer review ends in a relationship decision: keep, keep with conditions, or exit. If the customer review gives grounds to suspect money laundering, it goes to a suspicion assessment by the MLRO or nominated officer.
The fourth figure shows the path from match to decision. A material true match is attached to the customer risk profile with the article, the stage and the analyst's summary. When the match changes the risk picture, the customer risk profile opens a customer review before the next scheduled date. The customer review may apply enhanced due diligence, such as source of wealth questions or more frequent monitoring. The customer review ends in a relationship decision: keep, keep with conditions, or exit. If the customer review gives grounds to suspect money laundering, it goes to a suspicion assessment by the MLRO or nominated officer under your internal reporting procedure.
The EBA guidelines give the EDD side of that review. In high risk situations, the appropriate type of EDD, including the extent of the additional information sought, and of the increased monitoring carried out, will depend on the reason why an occasional transaction or a business relationship was classified as high risk. For retail banks, they list obtaining more information about the customer and the nature and purpose of the business relationship to build a more complete customer profile, for example by carrying out open source or adverse media searches or commissioning a third party intelligence report. The FCA lists establishing how the customer or beneficial owner acquired their wealth to be satisfied that it is legitimate among its examples of EDD.
The EU AML Regulation sets the timing frame for updates. Under Article 26, the period between updates of customer information must not exceed 1 year for higher risk customers under enhanced measures and 5 years for all other customers, and firms must review the information sooner where there is a change in the relevant circumstances of a customer or where they become aware of a relevant fact which pertains to the customer. In our reading, a credible story about a customer's involvement in fraud is that kind of relevant fact, so your policy should say how quickly a review opens after a material match.
There is one more question the Wolfsberg FAQs ask you to treat separately: reputational risk. They give the example of a corporate customer whose owners face allegations that EDD shows to be false. The FI would be able to demonstrate and explain, where necessary, the steps it had taken and the basis on which it accepted the relationship, but it would not necessarily be able to mitigate the Reputational Risk in the same manner. Their conclusion is that the Reputational Risk element should therefore be assessed and considered in its own right and any decision taken accordingly by the relevant risk owner(s). Your escalation route should name who owns reputational risk decisions, which may not be the MLRO.
What should the decision record show?
The decision record is what an examiner samples. The Wolfsberg FAQs list recording of outcomes and rationale among the procedure topics, providing requirements for a clear demonstration of the logic applied in alerts assessment and the rationale for decisioning made in respect of all alerts (including true and false positive matches) subject to review. Note the scope: all alerts, including false positives. A list of cleared hits with no reasons isn't a record.
Based on the sources in this guide, we'd expect each closed alert to show:
- the name screened, the screening run and the date;
- the article or record, saved, with its source and publication date;
- the identifiers compared and the result of the identity check;
- the risk category and the stage the story had reached;
- the materiality decision and the reason for it, in a sentence;
- who closed it, or which approved rule closed it;
- for a material match, what changed in the risk profile and which review it opened.
This list is our reading, not a rule. Each item traces to a source: the outcome and rationale requirement in the Wolfsberg FAQs, the archive and traceability criteria they set for systems, and the EU requirement to distinguish allegations from convictions.
Saving the article matters more than it looks. The Wolfsberg evaluation criteria include Archive: accessibility of media articles which are archived or no longer available in open sources. A link that no longer works can't support a decision a year later.
Retention follows your AML record-keeping rules. Under Article 77 of the EU AML Regulation, the information has to be retained for a period of 5 years commencing on the date of the termination of the business relationship, and personal data deleted when that period ends, unless another retention rule applies or a competent authority requires longer. The EU rules also limit what you do with the data. Under Article 76, personal data may be processed on the basis of the Regulation only for the prevention of money laundering and terrorist financing, and the processing of personal data on the basis of this Regulation for commercial purposes shall be prohibited. Adverse media files shouldn't feed marketing or credit decisions that the AML purpose doesn't cover.
How do you test the control and report on it?
A framework without testing drifts. The Wolfsberg FAQs describe two kinds of check: QC is performed as a preventative control (pre-alert outcome determination), while QA is deemed a detective control (post-alert outcome determination). A strong control framework will contain elements of both. Where an FI can dedicate a proportionate degree of resources to quality check or quality assure selected alerts, a statistical based sampling should be viewed as the target approach.
The FAQs' quality assurance list covers systems and processes. For systems, it includes the quality and completeness of records returned from screening, an assessment of adequacy of system risk parameters and alert filtering mechanisms, and evaluation of the performance of the screening application by assessing the precision of screening and its hit rate. For processes, it includes checking that the total number of alerts generated matches the total of alerts worked on, and monitoring and testing of the false positive alert population to ensure there are no missed true matches.
That last test matters most for rules. Reporting how many alerts were closed is easy. Showing that a sample of closed alerts, including those closed by rules, contained no real hits is harder, and it's the test that finds a rule that is closing too much.
For management, the FAQs list screening volume, volume of alerts generated, false positives and true matches, quality assurance outcomes, and the relationships reviewed and exited by the FI due to NNS. We'd add three measures that tie the control to the framework: the share of in-scope customers screened on schedule, the time from a material match to an opened review, and the number of auto-discount rules past their review date.
What should adverse media screening software do?
Software can't make the eight decisions for you. It should make them visible, apply them consistently and keep the evidence. The Wolfsberg FAQs list what to assess when evaluating a screening solution, and we'd use them as the core of any request for proposal:
| Criterion | What to ask the vendor to show |
|---|---|
| Coverage | Media sources in the markets where your customers are, including local-language sources |
| Data | Completeness and timeliness, and how duplicate coverage of one story is grouped |
| Matching | Name matching on your own sample, with the false positive rate and the identifiers used |
| Archive | Saved copies of articles that are later removed from the web |
| Translation | Summaries in your analysts' language, with the original kept |
| Scalability | Control over search parameters, depth and filtering by segment |
| Reporting | Management information that matches your framework |
| Traceability | A record of every screening event, configuration and rule that produced or closed an alert |
| Data sharing | Where screening or adjudication happens, and under which data protection terms |
Two further tests come from the rules rather than the FAQs. First, can the system record the stage of each story (allegation, investigation, charge, conviction) and carry it into the risk profile? Under the EU AML Regulation that distinction is a condition for processing the data. Second, who decides? Article 76 of the regulation allows decisions resulting from automated processes, including AI systems, only on conditions. One is that any decision to enter or refuse to enter into or maintain a business relationship with a customer, or to increase or decrease the extent of the customer due diligence measures, is subject to meaningful human intervention to ensure the accuracy and appropriateness of such a decision. Another is that the customer may obtain an explanation of the decision and challenge it, except in relation to a suspicious transaction report. A tool that closes immaterial stories by approved rule is one thing. A tool that changes a customer's risk rating or exits a relationship on its own is another, and it shouldn't pass your evaluation.
Ask every vendor to run on a sample of your own customers, including a few you know have relevant news and a few with very common names. Then ask them to explain three closed alerts and one escalated alert, from the record alone.
If you need a way to see how adverse media feeds the rating once a hit is confirmed, the Customer Risk Rating Matrix gives teams a structured, repeatable method to score each customer's risk level across standard CDD dimensions, assign a risk tier (low, medium, high, or very high), and determine whether standard or enhanced due diligence applies. It treats adverse media as one weighted factor and says plainly that the matrix captures PEP status and adverse media as risk factors, but those inputs should come from a dedicated screening program.
Who decides what in adverse media monitoring?
The sources in this guide put the decisions with people. The Wolfsberg FAQs describe a tiered model in which subsequent levels may be utilised where alerts cannot be discounted, or positive matches are identified, and due to the subjective nature of NNS outputs, require specialist subject matter expertise and input. The EU AML Regulation requires meaningful human intervention for relationship decisions and for changes to the extent of due diligence. Software, including AI agents, can do most of the reading, matching and preparing. The decisions stay with the accountable people.
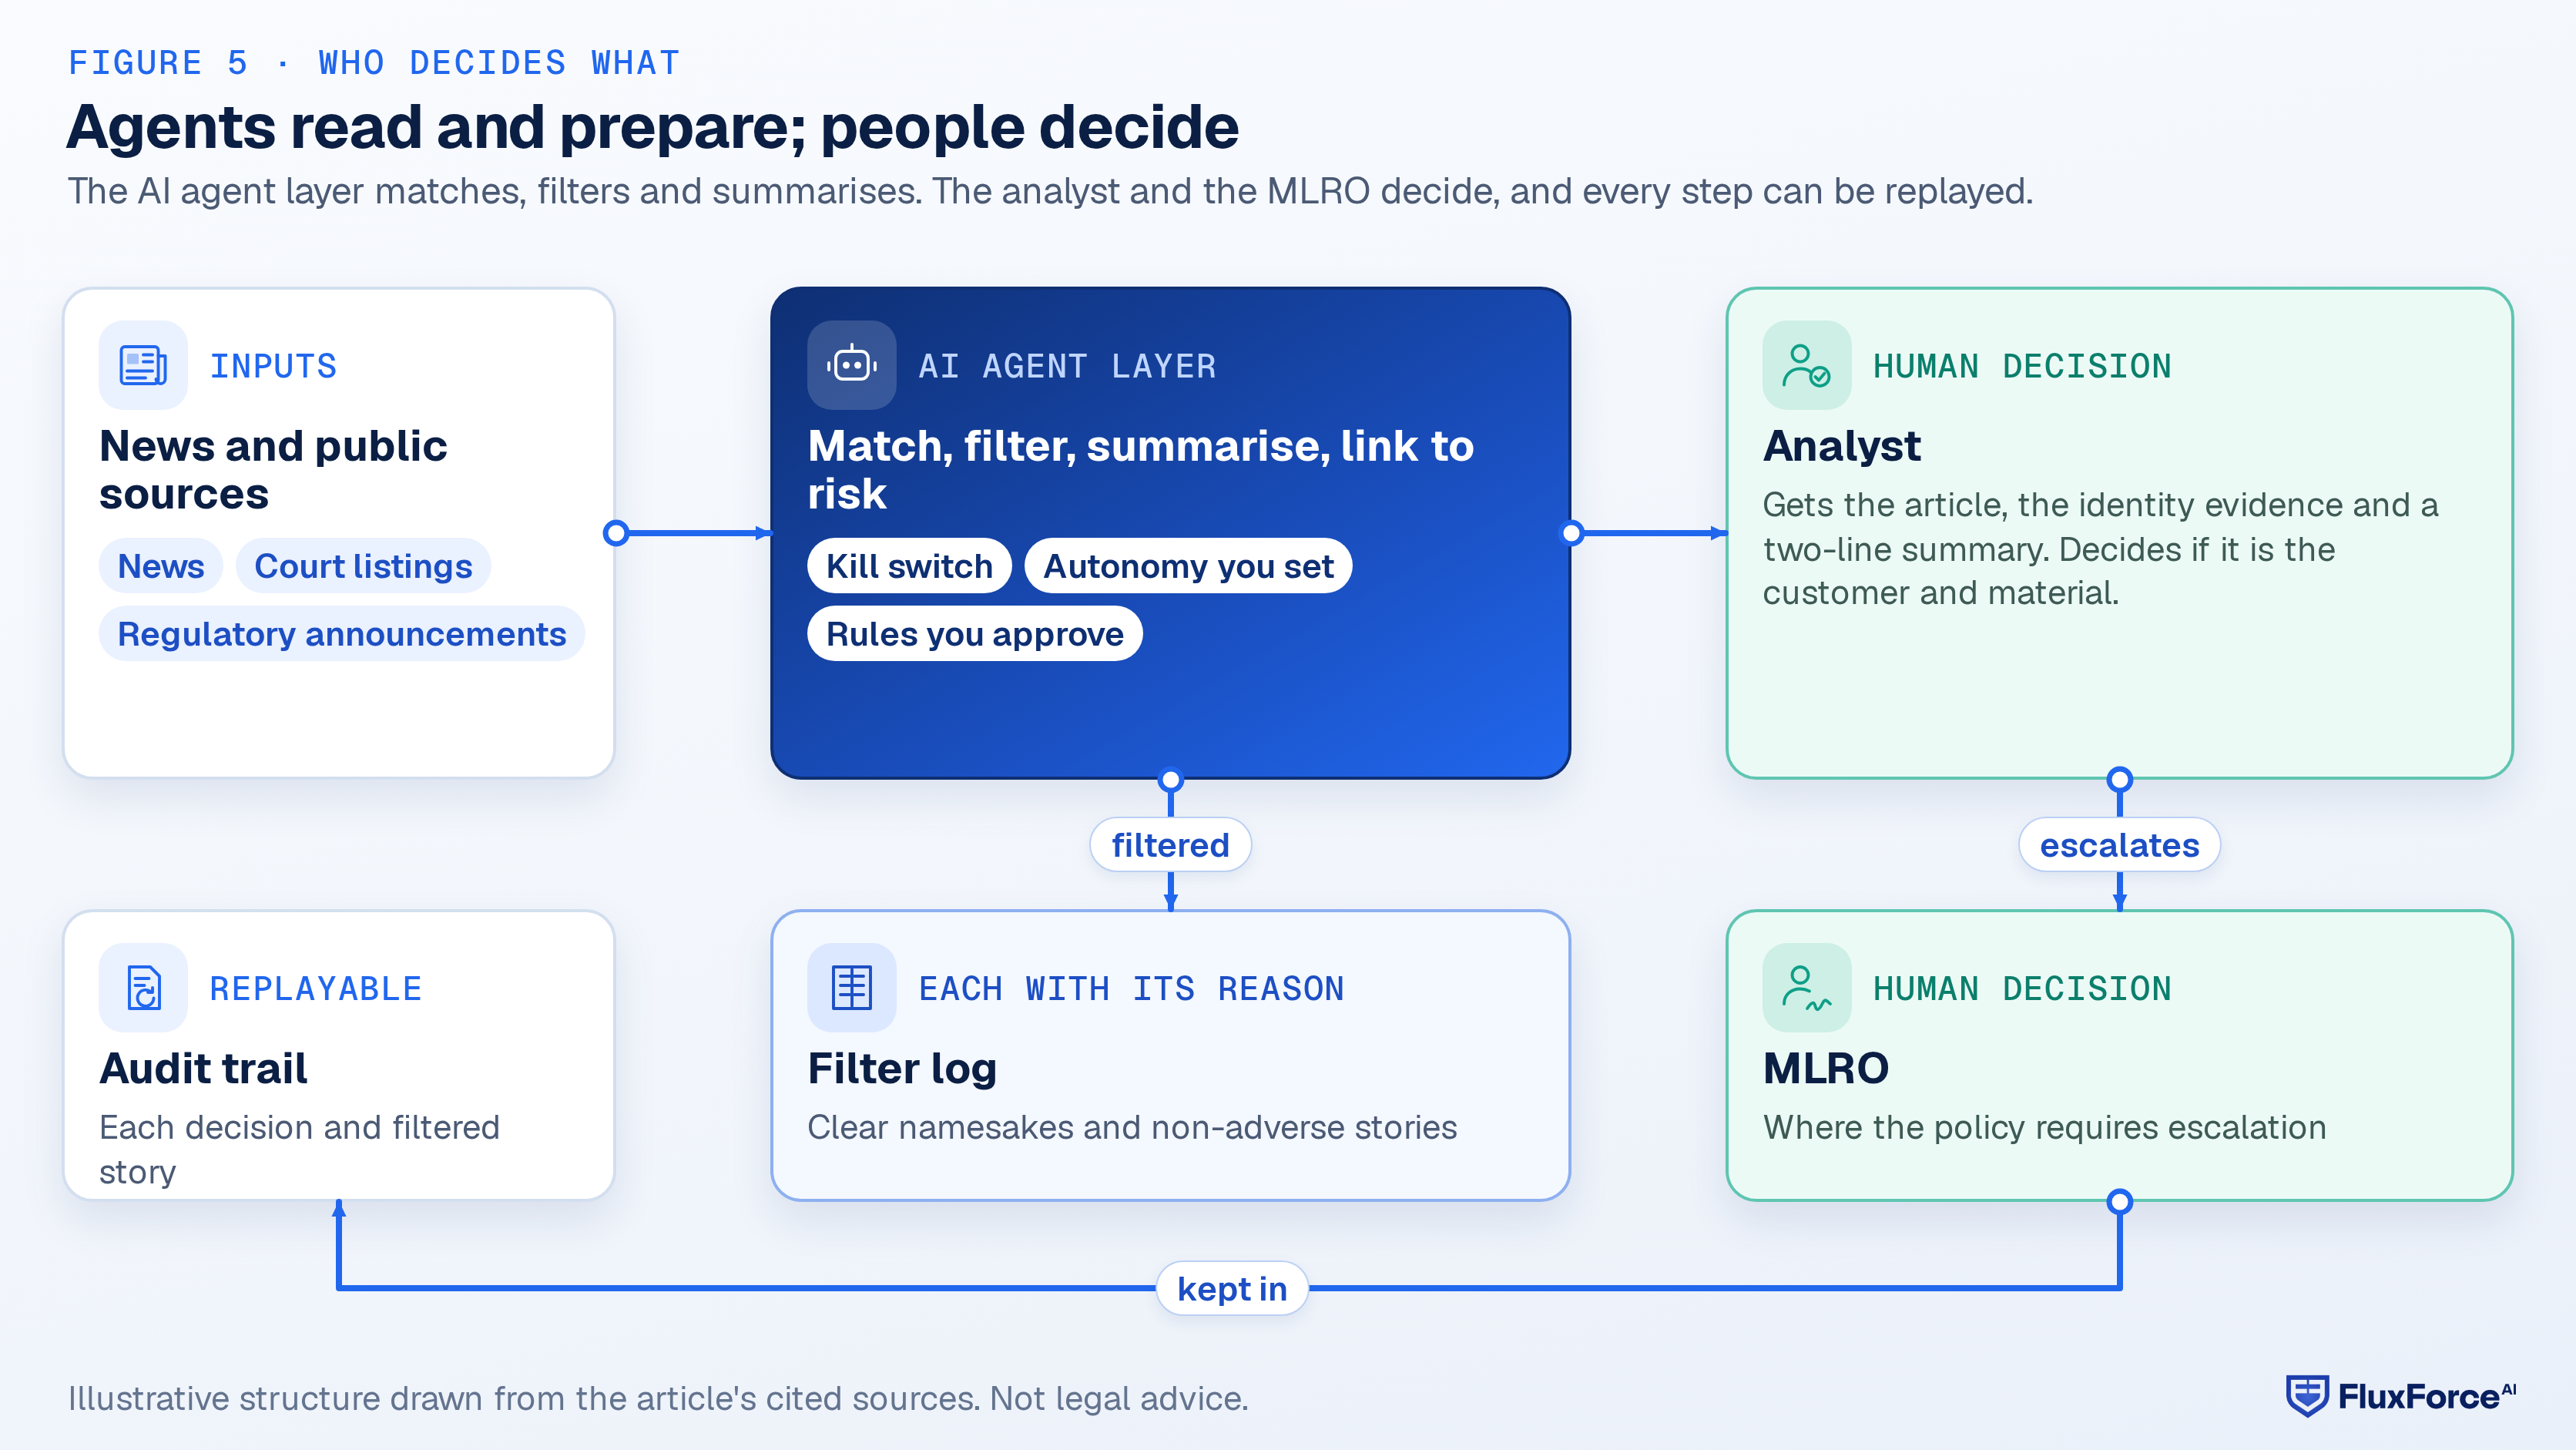
- News and public sources, including court and regulatory announcements, go into the AI agent layer. The AI agent layer filters clear namesakes and non-adverse stories under rules you approve and writes each one to the filter log with its reason. Anything that could affect risk goes from the AI agent layer to the analyst with the article, the identity evidence and a two-line summary. The analyst decides whether the story is about the customer and material, and escalates to the MLRO where the policy requires it. The MLRO decision, the analyst decision and every filtered story are kept in the audit trail, so an examiner can replay any of them.
The fifth figure shows where an AI agent layer fits. News and public sources, including court and regulatory announcements, go into the AI agent layer. The AI agent layer filters clear namesakes and non-adverse stories under rules you approve and writes each one to the filter log with its reason. Anything that could affect risk goes from the AI agent layer to the analyst with the article, the identity evidence and a two-line summary. The analyst decides whether the story is about the customer and material, and escalates to the MLRO where the policy requires it. The MLRO decision, the analyst decision and every filtered story are kept in the audit trail, so an examiner can replay any of them.
- No rule cited here mandates "adverse media screening" by name; the expectation comes from understanding customer risk and keeping CDD current.
- The EBA says the absence of criminal convictions alone may not be sufficient to dismiss allegations, so a conviction-only alert line needs a written reason.
- From 10 July 2027 the EU AML Regulation allows criminal offence data to be processed only from reliable sources, with procedures that distinguish allegations, investigations, proceedings and convictions.
- Close alerts for two separate reasons, false positive or immaterial, and record the rationale for every alert, including rule-closed ones.
- Software should match, filter and keep the evidence; people judge materiality and decide on the relationship and on suspicion.
Conclusion
Adverse media screening is a risk-based control with no fixed template. The FATF standard expects ongoing due diligence that keeps your knowledge of the customer current, and the EBA guidelines and the FCA guide go further: they name reputation as a risk factor and expect firms to act on credible allegations. The EU AML Regulation will require you to keep allegations and convictions apart from July 2027, and the US bank rule leaves the design to your own procedures. The Wolfsberg FAQs supply most of the design: scope, categories, stages, sources, discounting, materiality, records and testing.
The framework works when each of those choices is written down, owned and tested, and when every closed alert can explain itself. Before you change tools, write the eight decisions down. Then ask any vendor to show you, from the record alone, why three of your own alerts were closed and why one was escalated.
Request the adverse-media monitoring control matrix and a shadow-mode run
Frequently Asked Questions
About the author
Sahil Kataria
Founder and CEO of FluxForce
Share this article